


Hear From Our Customers
I have been incredibly impressed with how you handle high-pressure cases and situations. Your ability to maintain absolute accuracy while working under tight deadlines ensures our operations run smoothly.

Income Tax Department (ITD)
Bikaner - RajasthanOur Bank needed an Information Technology Asset Management Solution. ECS team has implemented the complete solution with ease. I Must say ECS team support team is also very responsive and operates 24×7.

Paresh Kelawala – AGM IT
The Varaccha Co-operative Bank Ltd.The digital forensic engineer is well-versed with the data extraction of electronic devices and completed his work in a timely manner & in the best possible professional manner.

Directorate of Revenue Intelligence (DRI)
Surat - GujaratIf you are looking for an easy solution without buying servers and moreover maintaining the complete infrastructure in your office, ECS will certainly offer you a very simple, reliable, cost-effective and efficient solution.

Chintan Shah – Director
Veritas Insurance Services Pvt. Ltd.The team was hardworking and competent. They managed the forensic affairs smoothly.
Income Tax Department (ITD)
Bareilly - Uttar PradeshECS is the most trusted IT partner for us!!
ECS offered us the most advance, secure, scalable & reliable options with flexible server configuration in their most advanced Tier 4 data center. Their 24*7*365 NOC is always very much customer friendly & dedicated to their solutions.

Kuntal B. Parikh – CEO- IT Director
Civic InfotechECS Infotech Pvt. Ltd. has successfully rendered their digital forensic services during the various requirement of our department. Their team of experts delivered excellent digital forensic services. We also appreciate professionalism, dedication and high-quality services delivered by ECS team, importantly with in a stipulated time frame. We found their services satisfactorily.

Enforcement Directorate (ED)
Indore - Madhya PradeshThe work done by the forensic team is commendable and the team completed the work ahead of schedule.
Income Tax Department (ITD)
Bhilwara - RajasthanECS team is professional, experience & has certified cybersecurity experts They provide enterprise-grade cybersecurity solutions with the best support.
We highly recommend ECS as a strong Cyber Security company. We are happy to have a long-term business relationship.

Mr. LR. Modhavadiya – HOD , IT Manager
Saurashtra Cement
How Surat National Bank Strengthened Its Cyber Defenses with ECS Anti-Phishing & Anti-Rogue Solution
TABLE OF CONTENTS Client Overview Challenges Faced The ECS Anti-Phishing & Anti-Rogue Solution Impact and Results Client Testimonial Conclusion Client

From Dead Device to Digital Evidence: Chip-Off Forensics in Action
TABLE OF CONTENTS Overview Client Background Challenges Solution Delivered Outcome or Results Conclusion Overview When standard data extraction techniques fail

Clinical Research Organisation Secures Confidential Data with ECS’ Advanced Email Security Solutions
Company Overview The client, a globally renowned clinical research organisation, is a trusted partner to the pharmaceutical industry. Known for

Banking on Cyber Safety: Prime Cooperative Bank’s Success with Anti-Rogue Solution
Overview Prime Cooperative Bank Surat partnered with us to implement a comprehensive Anti-Phishing and Anti-Rogue Solution, aimed at safeguarding its

Inside the Threat Intelligence Revolution: ECS Secures Financial Operations
Overview The Global Financial Holdings is a company that provides globally some of the best and most developed financial services

Securing Banking Operations with ECS SOC Services
Overview At a time when cyber threats are increasingly becoming complex and frequent, financial institutions should take a proactive approach

Tracing Stolen Crypto Assets Using ECS InfoTech’s Advanced Cryptocurrency Investigation Solutions
TABLE OF CONTENTS Introduction Background Challenges Our Approach Results Client Testimonial Conclusion Introduction In today’s rapidly evolving digital finance landscape,

Inside ECS’s Digital Forensics Response to a High-Stakes Ransomware Attack
Introduction At present, businesses face cyber threats that threaten sensitive data and disrupt operations, with Digital Forensic Services becoming essential

100% Data Recovery Services That Revived a Damaged Seagate 1TB Drive
Client Requirement At ECS, a leading data recovery company, we recently received a distress call from a client regarding a

ECS Solved a High-Stakes Data Breach with Digital Forensics Services
A leading Indian IT solutions provider recently encountered a critical data breach that put confidential client information and proprietary technology
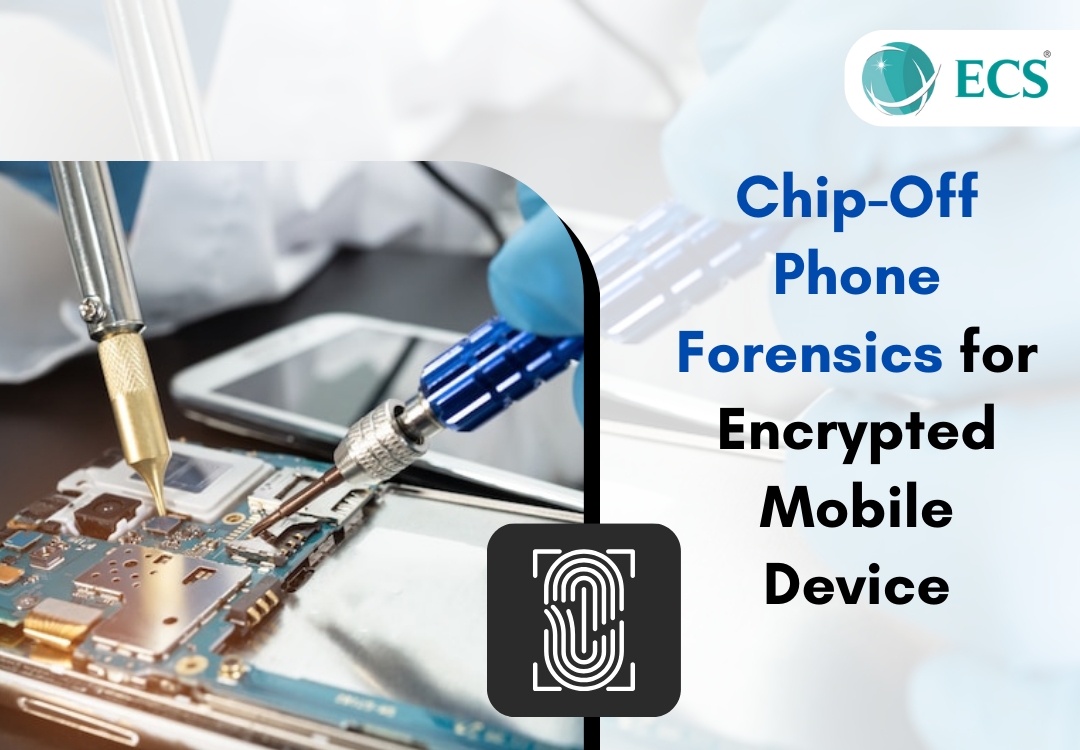
Chip-Off Phone Forensics for Encrypted Mobile Device
Client Requirement Our client needed to recover critical data from a highly encrypted mobile device. Traditional methods failed due to

Rogue Anti Malware: The Game-Changer in Fintech Cybersecurity & RBI Compliance
Client Overview: A leading Fintech corporation sought a robust cybersecurity strategy to align with RBI compliance regulations. Facing constant cyber

Strengthening Cybersecurity for a Fintech Corporation with Advanced CSOC Services
A leading digital payment and financial management solutions company based in Mumbai, India, faced rising cybersecurity threats. With sensitive financial

Revolutionizing Healthcare Security with Cyber Threat Intelligence Solutions
Client Overview Our client, a well-known healthcare provider, runs a network of hospitals and diagnostic centers across the country. With

Banking on Security: How ECS Infotech Delivers Cutting-Edge Cyber Threat Intelligence Solutions
Client Overview A leading financial institution faced a growing challenge from cyber threats targeting sensitive customer data and critical banking

Resolving Complex Financial Fraud with Expertise in Financial Forensics Investigation
TABLE OF CONTENTS Client Overview Challenges Faced Our Approach Results Delivered Client Testimonial Conclusion Client Overview A large real estate

Advanced Data Recovery Forensics for a Multinational Retail Corporation
Introduction In the age of digital transformation, businesses across industries rely heavily on data to drive operations and decision-making. However,

Advanced Audio and Video Forensics Services for Resolving a Corporate Dispute
Client Background Our client, a prominent legal firm, was engaged in a corporate dispute where audio and video evidence were
Enhancing Insider Threat Monitoring to Mitigate Insider Cyber Threats
Client Overview A prominent mid-sized IT company specializing in managing sensitive client data approached ECS to investigate potential insider cyber

Strengthening Email Security for a Leading Financial Institution with ECS Cloud Email Security Solution
Client Background A well-established financial institution offers a wide range of banking and financial services to individuals and corporations. With

Strengthening Cyber Threat Intelligence and Mitigating Insider Threats for a Leading Financial Institution
Client Background A leading financial institution in India faced escalating concerns around potential insider threats, which posed a high risk

Uncovering the Truth: How Social Network Forensics Helped Stop a Major Data Breach
Client Overview Our client is a leading real estate company, known for handling multiple high-value projects across India. Recently, they

Unmasking the Breach: How Cloud Forensics Solutions Secured a Leading Healthcare Provider’s Data Client
Overview Our client, a leading healthcare provider with multiple branches across India, faced a critical data breach that affected their

Resolving a Legal Dispute with Mobile Device Forensics
Client Background: A leading law firm approached ECS Infotech to assist in a legal dispute where a key piece of

Advanced Network Forensics Investigation for an E-commerce Platform
Client Background: A leading e-commerce platform in India was experiencing a significant disruption in its operations due to a sudden

Uncovering Corporate Data Theft with Forensic Disk Recovery
Client Background: Our client a prominent technology firm, faced a severe data breach when sensitive corporate information, including confidential project
Uncovering Data Leaks: A Case Study in Social Media Forensics for the Real Estate Industry
Client Background: A real estate organization, our client, faced a problem when it suspected an internal security threat. They believed

Addressing Insider Threats with Advanced Insider Risk Management Software
Client Background Retail Corp is a large retail Company with numerous stores all over the country and an online store;

Unveiling Clarity: Tailored Audio-Video Forensics for Investigative Excellence
Client Overview Our client, an established investigative company that deals majorly in corporate fraud and criminal investigation, has encountered rigorous

Strengthening Email Security and Conducting Forensic Investigations
Client Background A special company, which operates in the context of logistics and supply chain management experienced a lot of

Uncovering and Recovering from Financial Fraud
Client Background A leading retail company faced a significant challenge when it discovered discrepancies in its financial records, indicating potential

Advanced Forensic Hard Drive Recovery Solutions for Law Firm
Overview Our client is a prominent legal practice specializing in corporate law, experienced an unexpected hardware failure, resulting in the

Solving Complex Cases: The Critical Role of Audio and Video Forensics in Modern Investigations
TABLE OF CONTENTS Project Overview Challenge Solution Results Conclusion Project Overview In 2023, a high-profile criminal case hinged on the
Instant Response and Recovery with ECS Infotech’s Cloud Forensics Solutions for a Global E-Commerce Company
Global e-commerce companies operate in this digitized world, where there is a big challenge to secure their cloud environments. When

Guarding Financial Fortresses: How ECS Insider Investigation Services Shielded a Leading Firm from Insider Threats
Overview Insider attacks pose a serious concern to the cybersecurity of enterprises in today’s digital environment. ECS Infotech is a top provider of insider

Unveiling Cyber Intrusion: A Case Study in Advanced Network Forensics
Introduction Businesses today rely significantly on network infrastructure to run effectively in the age of digital reliance. However, there are

Unlocking Justice: A Case Study in Forensic Cell Phone Data Recovery
Client Background Our Client is a lawyer specializing in intellectual property law, working for a prominent firm in a bustling

Unmasking Financial Fraud: A Forensic Investigation
Introduction In today’s interconnected digital landscape, the risk of financial fraud looms large over organizations. ECS Infotech was approached by

Uncovering Digital Evidence through Social Media Forensics
TABLE OF CONTENTS Introduction Client Background Challenges Solution Delivered Results Conclusion Introduction In the age of digital communication, social media
Resolving Legal Disputes with Advanced Audio Video Forensics Services
Client Background Client Investigations is a renowned private investigative firm based in metropolitan area, specializing in a wide range of

Enhancing Law Enforcement Investigations through Advanced Hard Disk Forensics
TABLE OF CONTENTS Overview Client Challenge ECS Solution Services Provided Hard drive Recovery Disk Forensics Key Results Conclusion Overview In

Enhancing Cybersecurity Measures in Healthcare: A Case Study
Overview The healthcare sector has relied more and more on digital technologies in recent years to improve patient care and

Unlocking Justice: A Case Study in Forensics Phone Recovery for Critical Legal Data Retrieval
Introduction With so much private and sensitive data on them, mobile devices have become an essential part of our lives

Uncovering Elusive Financial Fraud
Overview Our client is a reputable global conglomerate, contacted us to initiate a financial fraud investigation after detecting irregularities in their

Anti-phishing and Anti-rogue Solution For Leading Banks Of Gujarat
TABLE OF CONTENTS Overview Case Challenges How ECS Provided Solution to various Banks? Results Conclusion Overview According to RBI guidelines,

Cyber Forensics Solution Provided to a Manufacturing Company
Overview In today’s ever-changing and emerging technological world, Cyber forensics has become an important step in criminal investigations. This typically

ECS Provided a Complete CSOC Solution to a Bank
Overview Our client is a reputed industrialist and runs a co-operative bank. He has been working in the bank for

Cyber Security Consulting Service to a Reputed Manufacturing Company
Overview Our client is in the manufacturing industry, and his company is in the emerging stage where they are growing

How ECS Helped Retrieve Deleted WhatsApp Chat Messages For a Law Enforcement Agency?
TABLE OF CONTENTS Case Overview Case Challenges How did ECS Provide a Solution? Result Conclusion FAQ’s Case Overview Client is

ECS’ audio and video forensics expertise helped a law enforcement agency with face recognition of the culprit
Case Overview The customer require audio-video evidence from the scene of the crime. Our client is one such law enforcement

How Kaspersky Endpoint Security Solution Was Used To Strengthen Network Security
Company Overview The client is a leading technology solutions provider offering services in mobile and web applications and enables businesses

Clinical Research Organisation Chooses ECS’ Email Security Solution to Protect Confidential Data and Combat Malicious Intrusions via Emails.
Company Overview Client is an independent clinical research organisation that creates in-depth scientific know-how, technical edge and better foresight for

Large Co-operative Bank Was Secured By ECS Mobile Device Management
Overview This Bank has a spectacular growth in the nearly 40 years of time span having more than 20+ branches

VAPT for Compliance: How Security Testing Helps Meet ISO 27001, PCI DSS, RBI, CERT-In & DPDP Requirements
Strengthen compliance with ISO 27001, PCI DSS, RBI, CERT-In & DPDP through VAPT. Identify security gaps, reduce risks & meet

How to Evaluate a VAPT Report: A Practical Guide for CTOs, CISOs & IT Managers
How to evaluate a VAPT report effectively. Learn how CTOs, CISOs and IT managers can assess vulnerabilities, risks, findings and

API Security Testing Checklist: Complete API Penetration Testing Guide for Secure APIs
Secure your APIs with our complete API Security Testing Checklist. Learn API penetration testing steps, common risks, OWASP API Top

VAPT Testing Compliance Guide: PCI DSS, RBI, ISO 27001 & SOC 2 Requirements
Understand VAPT testing compliance for PCI DSS, RBI, ISO 27001 & SOC 2. Learn requirements, benefits and how VAPT helps

Why VAPT Testing Is Essential for Cyber Security Compliance & Business Protection
Ensure cyber security compliance with VAPT testing. Identify vulnerabilities, reduce risks, protect business data, and meet regulatory requirements.

Top 10 Most Trusted VAPT Companies in India (2026) – Compare Services, Costs & Security Expertise
Discover the top 10 trusted VAPT companies in India (2026). Compare services, pricing, expertise, certifications, and choose the best cybersecurity

VAPT Testing Cost: Pricing Guide for Web, API & Cloud Security Assessments
VAPT testing cost explained: compare pricing for web, API, and cloud security assessments. Learn key factors, pricing models, and budgeting

VAPT in Cybersecurity: Audit Types, Methodology and Benefits
Learn VAPT in cybersecurity, including audit types, testing methodology and key benefits for identifying vulnerabilities and strengthening security.

How Often Should You Perform VAPT? A Complete Guide for Businesses
Learn how often businesses should perform VAPT, what affects testing frequency, and how regular assessments help reduce cyber risks and

VAPT Services: Types of Penetration Testing, and Key Benefits
Strengthen security with VAPT services, including network, web, and mobile penetration testing to identify vulnerabilities and reduce cyber risks.

VAPT: Vulnerability Assessment and Penetration Testing (Types)
Explore types of VAPT—Vulnerability Assessment and Penetration Testing—to identify, assess, and secure systems against evolving cyber threats effectively.

Vulnerability Scanning Price in India: Complete Cost Breakdown for 2026
Discover vulnerability scanning costs in India for 2026, detailed pricing, factors, tools, and service comparisons to help you choose the

Common Security Risks in Indian Businesses & How VAPT Services Prevent Cyber Attacks
Protect your business from cyber threats. Discover common security risks in Indian companies and how VAPT services help prevent attacks

Core Components of VAPT: Services, Process, and Security Advantages
Core components of VAPT explained services, step-by-step process, and key security advantages to strengthen cybersecurity and protect your business from

Why Every Organization Needs VAPT Solutions to Prevent Data Breaches
Why every organization needs VAPT solutions to prevent data breaches, strengthen cybersecurity, reduce risks, and protect sensitive business data.

How VAPT Solutions Help Organizations Prevent Cyber Attacks in 2026
Learn how VAPT solutions in 2026 help organizations identify vulnerabilities, strengthen security posture, and proactively prevent advanced cyber attacks.

Ultimate Guide to VAPT Services & Pricing in India (2026)
Comprehensive 2026 guide to VAPT services in India—types, methodology, compliance requirements, pricing models, and how to choose the right provider.

VAPT Audits: A Complete Guide to Methods, Pricing & Security Advantages
Comprehensive guide to VAPT audits covering methods, costs, pricing models, and key security benefits to protect systems from vulnerabilities.

How to Select the Best VAPT Service Provider: Essential Criteria for Modern Businesses
Learn how to choose the best VAPT service provider with key criteria like expertise, tools, compliance, reporting quality, and post-test

Vulnerability Assessment & Penetration Testing (VAPT): Strengthening Your Cybersecurity Defense in 2026
Discover how Vulnerability Assessment and Penetration Testing (VAPT) can fortify your cybersecurity defense in 2026. Learn its benefits, types, and

Comprehensive Guide to VAPT Services in India: Why Expert Consulting and Auditing Matter
Discover top VAPT Services in India with expert consulting and auditing. Ensure your business’s cybersecurity through comprehensive vulnerability testing.

How Much Does Penetration Testing Cost in 2025? A Complete Pricing Guide
Find out how much penetration testing costs in 2025, from pricing in India to global rates, and learn what impacts

Why Do You Need VAPT? Top Reasons Every Business Must Prioritize Security Testing in 2026
Learn why VAPT is crucial in 2026. Identify vulnerabilities, prevent cyber threats, and protect your business with effective security testing

Vulnerability Assessment & Penetration Testing: Key Differences and How VAPT Services Protect Your Business
Discover the key differences between vulnerability assessment & penetration testing, and how VAPT services strengthen security to protect your business.

The Future of VAPT Services: Automation and Evolving Threats in 2026
Explore VAPT Services in 2026 using automation to tackle evolving threats, enhance security efficiency, and strengthen business resilience.

VAPT Testing Explained: Why Your Business Needs It for Cyber Defense
Learn VAPT Testing to uncover vulnerabilities, prevent cyber threats, and strengthen your business security with expert cyber defense strategies.

A Comprehensive Guide to Vulnerability Assessment & Penetration Testing (VAPT Services) in India
Learn Vulnerability Assessment & Penetration Testing to identify risks, tools, and processes. Strengthen security with VAPT services in India effectively.

VAPT: Complete Guide to Vulnerability Assessment and Penetration Testing
Learn what VAPT means, how vulnerability assessment and penetration testing work, VAPT types, process, tools, benefits, costs, reports and security

VAPT Audit: Complete Guide to Process, Checklist, Report & Compliance
Learn what a VAPT audit is, how the audit process works, what a VAPT report and checklist include, key compliance

Vulnerability Assessment: Benefits, Process, Tools & Complete Guide
Learn what vulnerability assessment is, its benefits, process, tools and cost. Discover how vulnerability scanning identifies security weaknesses and supports

VAPT Testing: Complete Guide to Services, Process, Cost & Security
Learn what VAPT testing is, how vulnerability assessment and penetration testing work, what VAPT services cover, how much testing can

Why Transparency Sets the Best VAPT Companies in India Apart
Learn how the Best VAPT Companies in India stand out through transparency, delivering clear insights, reliable testing, and stronger cybersecurity

How Your Digital Assets Are Secured When You Select the Correct VAPT Service Provider
Learn how a trusted VAPT Service Provider secures digital assets through vulnerability assessment, penetration testing, and proactive threat protection.

Top 7 Reasons Why MNC’s and SME’s Need VAPT
Discover why VAPT is essential for MNCs and SMEs. Learn 7 key reasons to strengthen security, identify vulnerabilities, and protect

What are the different types of penetration testing?
Learn different types of penetration testing to identify vulnerabilities, improve security, and protect systems from cyber threats and attacks effectively.

How VAPT Benefits the Healthcare Industry?
VAPT Benefits healthcare by identifying vulnerabilities, protecting patient data, and ensuring compliance with security standards to prevent cyber threats.

What Is VAPT? Benefits, Services, Solutions & Why Organizations Need It
Learn what VAPT stands for, its benefits, services and solutions, and why organizations need vulnerability assessment and penetration testing to

How Does VAPT Defend Against Data Breaches
VAPT helps identify vulnerabilities and prevent attacks. Learn how VAPT protects systems, reduces risks, and strengthens security against data breaches.

Continuous VAPT for SMEs: Why Ongoing Security Testing Matters
Learn why continuous VAPT is important for SMEs, including vulnerability scanning, penetration testing, cloud security, CI/CD and ongoing risk management.