


Hear From Our Customers
I have been incredibly impressed with how you handle high-pressure cases and situations. Your ability to maintain absolute accuracy while working under tight deadlines ensures our operations run smoothly.

Income Tax Department (ITD)
Bikaner - RajasthanThe digital forensic engineer is well-versed with the data extraction of electronic devices and completed his work in a timely manner & in the best possible professional manner.

Directorate of Revenue Intelligence (DRI)
Surat - GujaratThe team was hardworking and competent. They managed the forensic affairs smoothly.
Income Tax Department (ITD)
Bareilly - Uttar PradeshECS Infotech Pvt. Ltd. has successfully rendered their digital forensic services during the various requirement of our department. Their team of experts delivered excellent digital forensic services. We also appreciate professionalism, dedication and high-quality services delivered by ECS team, importantly with in a stipulated time frame. We found their services satisfactorily.

Enforcement Directorate (ED)
Indore - Madhya PradeshThe work done by the forensic team is commendable and the team completed the work ahead of schedule.
Income Tax Department (ITD)
Bhilwara - Rajasthan
How Surat National Bank Strengthened Its Cyber Defenses with ECS Anti-Phishing & Anti-Rogue Solution
TABLE OF CONTENTS Client Overview Challenges Faced The ECS Anti-Phishing & Anti-Rogue Solution Impact and Results Client Testimonial Conclusion Client

From Dead Device to Digital Evidence: Chip-Off Forensics in Action
TABLE OF CONTENTS Overview Client Background Challenges Solution Delivered Outcome or Results Conclusion Overview When standard data extraction techniques fail

Clinical Research Organisation Secures Confidential Data with ECS’ Advanced Email Security Solutions
Company Overview The client, a globally renowned clinical research organisation, is a trusted partner to the pharmaceutical industry. Known for

Banking on Cyber Safety: Prime Cooperative Bank’s Success with Anti-Rogue Solution
Overview Prime Cooperative Bank Surat partnered with us to implement a comprehensive Anti-Phishing and Anti-Rogue Solution, aimed at safeguarding its

Inside the Threat Intelligence Revolution: ECS Secures Financial Operations
Overview The Global Financial Holdings is a company that provides globally some of the best and most developed financial services

Securing Banking Operations with ECS SOC Services
Overview At a time when cyber threats are increasingly becoming complex and frequent, financial institutions should take a proactive approach

Tracing Stolen Crypto Assets Using ECS InfoTech’s Advanced Cryptocurrency Investigation Solutions
TABLE OF CONTENTS Introduction Background Challenges Our Approach Results Client Testimonial Conclusion Introduction In today’s rapidly evolving digital finance landscape,

Inside ECS’s Digital Forensics Response to a High-Stakes Ransomware Attack
Introduction At present, businesses face cyber threats that threaten sensitive data and disrupt operations, with Digital Forensic Services becoming essential

100% Data Recovery Services That Revived a Damaged Seagate 1TB Drive
Client Requirement At ECS, a leading data recovery company, we recently received a distress call from a client regarding a

ECS Solved a High-Stakes Data Breach with Digital Forensics Services
A leading Indian IT solutions provider recently encountered a critical data breach that put confidential client information and proprietary technology
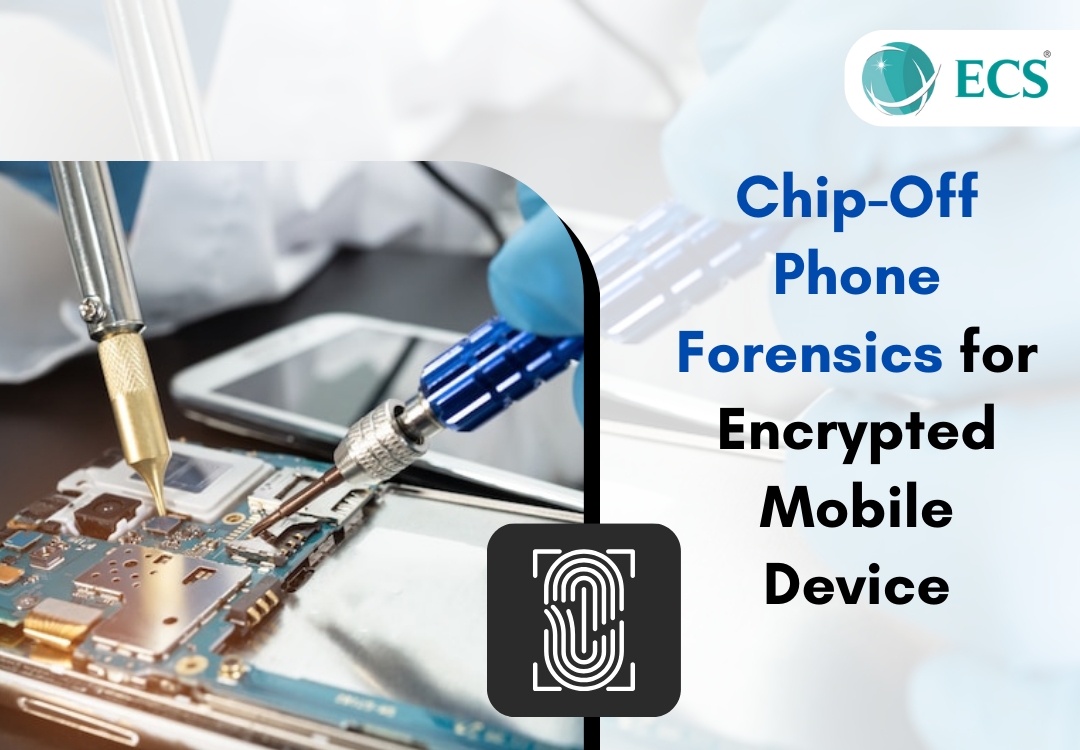
Chip-Off Phone Forensics for Encrypted Mobile Device
Client Requirement Our client needed to recover critical data from a highly encrypted mobile device. Traditional methods failed due to

Rogue Anti Malware: The Game-Changer in Fintech Cybersecurity & RBI Compliance
Client Overview: A leading Fintech corporation sought a robust cybersecurity strategy to align with RBI compliance regulations. Facing constant cyber

Strengthening Cybersecurity for a Fintech Corporation with Advanced CSOC Services
A leading digital payment and financial management solutions company based in Mumbai, India, faced rising cybersecurity threats. With sensitive financial

Revolutionizing Healthcare Security with Cyber Threat Intelligence Solutions
Client Overview Our client, a well-known healthcare provider, runs a network of hospitals and diagnostic centers across the country. With

Banking on Security: How ECS Infotech Delivers Cutting-Edge Cyber Threat Intelligence Solutions
Client Overview A leading financial institution faced a growing challenge from cyber threats targeting sensitive customer data and critical banking

Resolving Complex Financial Fraud with Expertise in Financial Forensics Investigation
TABLE OF CONTENTS Client Overview Challenges Faced Our Approach Results Delivered Client Testimonial Conclusion Client Overview A large real estate

Advanced Data Recovery Forensics for a Multinational Retail Corporation
Introduction In the age of digital transformation, businesses across industries rely heavily on data to drive operations and decision-making. However,

Advanced Audio and Video Forensics Services for Resolving a Corporate Dispute
Client Background Our client, a prominent legal firm, was engaged in a corporate dispute where audio and video evidence were
Enhancing Insider Threat Monitoring to Mitigate Insider Cyber Threats
Client Overview A prominent mid-sized IT company specializing in managing sensitive client data approached ECS to investigate potential insider cyber

Strengthening Email Security for a Leading Financial Institution with ECS Cloud Email Security Solution
Client Background A well-established financial institution offers a wide range of banking and financial services to individuals and corporations. With

Strengthening Cyber Threat Intelligence and Mitigating Insider Threats for a Leading Financial Institution
Client Background A leading financial institution in India faced escalating concerns around potential insider threats, which posed a high risk

Uncovering the Truth: How Social Network Forensics Helped Stop a Major Data Breach
Client Overview Our client is a leading real estate company, known for handling multiple high-value projects across India. Recently, they

Unmasking the Breach: How Cloud Forensics Solutions Secured a Leading Healthcare Provider’s Data Client
Overview Our client, a leading healthcare provider with multiple branches across India, faced a critical data breach that affected their

Resolving a Legal Dispute with Mobile Device Forensics
Client Background: A leading law firm approached ECS Infotech to assist in a legal dispute where a key piece of

Advanced Network Forensics Investigation for an E-commerce Platform
Client Background: A leading e-commerce platform in India was experiencing a significant disruption in its operations due to a sudden

Uncovering Corporate Data Theft with Forensic Disk Recovery
Client Background: Our client a prominent technology firm, faced a severe data breach when sensitive corporate information, including confidential project
Uncovering Data Leaks: A Case Study in Social Media Forensics for the Real Estate Industry
Client Background: A real estate organization, our client, faced a problem when it suspected an internal security threat. They believed

Addressing Insider Threats with Advanced Insider Risk Management Software
Client Background Retail Corp is a large retail Company with numerous stores all over the country and an online store;

Unveiling Clarity: Tailored Audio-Video Forensics for Investigative Excellence
Client Overview Our client, an established investigative company that deals majorly in corporate fraud and criminal investigation, has encountered rigorous

Strengthening Email Security and Conducting Forensic Investigations
Client Background A special company, which operates in the context of logistics and supply chain management experienced a lot of

Uncovering and Recovering from Financial Fraud
Client Background A leading retail company faced a significant challenge when it discovered discrepancies in its financial records, indicating potential

Advanced Forensic Hard Drive Recovery Solutions for Law Firm
Overview Our client is a prominent legal practice specializing in corporate law, experienced an unexpected hardware failure, resulting in the

Solving Complex Cases: The Critical Role of Audio and Video Forensics in Modern Investigations
TABLE OF CONTENTS Project Overview Challenge Solution Results Conclusion Project Overview In 2023, a high-profile criminal case hinged on the
Instant Response and Recovery with ECS Infotech’s Cloud Forensics Solutions for a Global E-Commerce Company
Global e-commerce companies operate in this digitized world, where there is a big challenge to secure their cloud environments. When

Guarding Financial Fortresses: How ECS Insider Investigation Services Shielded a Leading Firm from Insider Threats
Overview Insider attacks pose a serious concern to the cybersecurity of enterprises in today’s digital environment. ECS Infotech is a top provider of insider

Unveiling Cyber Intrusion: A Case Study in Advanced Network Forensics
Introduction Businesses today rely significantly on network infrastructure to run effectively in the age of digital reliance. However, there are

Unlocking Justice: A Case Study in Forensic Cell Phone Data Recovery
Client Background Our Client is a lawyer specializing in intellectual property law, working for a prominent firm in a bustling

Unmasking Financial Fraud: A Forensic Investigation
Introduction In today’s interconnected digital landscape, the risk of financial fraud looms large over organizations. ECS Infotech was approached by

Uncovering Digital Evidence through Social Media Forensics
TABLE OF CONTENTS Introduction Client Background Challenges Solution Delivered Results Conclusion Introduction In the age of digital communication, social media
Resolving Legal Disputes with Advanced Audio Video Forensics Services
Client Background Client Investigations is a renowned private investigative firm based in metropolitan area, specializing in a wide range of

Enhancing Law Enforcement Investigations through Advanced Hard Disk Forensics
TABLE OF CONTENTS Overview Client Challenge ECS Solution Services Provided Hard drive Recovery Disk Forensics Key Results Conclusion Overview In

Enhancing Cybersecurity Measures in Healthcare: A Case Study
Overview The healthcare sector has relied more and more on digital technologies in recent years to improve patient care and

Unlocking Justice: A Case Study in Forensics Phone Recovery for Critical Legal Data Retrieval
Introduction With so much private and sensitive data on them, mobile devices have become an essential part of our lives

Uncovering Elusive Financial Fraud
Overview Our client is a reputable global conglomerate, contacted us to initiate a financial fraud investigation after detecting irregularities in their

Anti-phishing and Anti-rogue Solution For Leading Banks Of Gujarat
TABLE OF CONTENTS Overview Case Challenges How ECS Provided Solution to various Banks? Results Conclusion Overview According to RBI guidelines,

Cyber Forensics Solution Provided to a Manufacturing Company
Overview In today’s ever-changing and emerging technological world, Cyber forensics has become an important step in criminal investigations. This typically

ECS Provided a Complete CSOC Solution to a Bank
Overview Our client is a reputed industrialist and runs a co-operative bank. He has been working in the bank for

Cyber Security Consulting Service to a Reputed Manufacturing Company
Overview Our client is in the manufacturing industry, and his company is in the emerging stage where they are growing

How ECS Helped Retrieve Deleted WhatsApp Chat Messages For a Law Enforcement Agency?
TABLE OF CONTENTS Case Overview Case Challenges How did ECS Provide a Solution? Result Conclusion FAQ’s Case Overview Client is

ECS’ audio and video forensics expertise helped a law enforcement agency with face recognition of the culprit
Case Overview The customer require audio-video evidence from the scene of the crime. Our client is one such law enforcement

How Kaspersky Endpoint Security Solution Was Used To Strengthen Network Security
Company Overview The client is a leading technology solutions provider offering services in mobile and web applications and enables businesses

Clinical Research Organisation Chooses ECS’ Email Security Solution to Protect Confidential Data and Combat Malicious Intrusions via Emails.
Company Overview Client is an independent clinical research organisation that creates in-depth scientific know-how, technical edge and better foresight for

Large Co-operative Bank Was Secured By ECS Mobile Device Management
Overview This Bank has a spectacular growth in the nearly 40 years of time span having more than 20+ branches

SOC Technical Aspects to Consider Before Buying SOC Services in 2026
Explore key SOC technical aspects to consider before buying SOC services in 2026, including SIEM, MDR, threat detection, automation, scalability,

Colocation Data Centers: Components, Offerings, and Business Advantages
Explore colocation data centers, their key components, services, and business benefits. Learn how colocation improves scalability, security, and uptime.

Data Recovery Cost in India (2026): HDD, SSD & RAID Recovery Prices Explained
Data recovery cost in India (2026) explained. Compare HDD, SSD & RAID recovery prices, factors, services and tips to choose

Insider Threat Detection: Types, Warning Signs, Tools & Prevention Strategies
Learn insider threat detection, types, warning signs, tools and prevention strategies to protect sensitive data, reduce risks and strengthen cybersecurity.

Top 10 Cyber Forensics Companies in India (2026): Services, Expertise & Comparison
Top 10 cyber forensics companies in India (2026), compared by services, expertise, technologies, and capabilities to help you choose the

Top 10 Data Recovery Companies in India (2026): Compare Hard Drive, SSD, RAID & Mobile Data Recovery Services
Compare the top 10 data recovery companies in India (2026) for HDD, SSD, RAID & mobile recovery services, expertise, costs,

Top 10 SOC Service Providers in India (2026): Compare Managed SOC Services, SIEM & 24/7 Security Monitoring
Discover the top 10 SOC service providers in India (2026). Compare managed SOC services, SIEM solutions, 24/7 monitoring, features, and

Top 10 Cyber Threat Intelligence Companies in India (2026): Compare Services, Threat Intelligence Platforms & Industry Expertise
Discover the top 10 cyber threat intelligence companies in India (2026). Compare threat intelligence platforms, services, expertise, and security solutions.

DPDP Act Compliance Gaps: What ISO 27001 Doesn’t Cover in 2026
Discover key DPDP Act compliance gaps that ISO 27001 may not cover in 2026, and learn how businesses can strengthen

How Digital Forensics Helps Organizations Recover from Cyber Incidents
Discover how digital forensics helps organizations investigate cyber incidents, recover critical evidence, identify threats, and strengthen cybersecurity defenses.

How Cyber Intelligence Helps Organizations Detect Threats Before They Become Attacks
Discover how cyber intelligence helps organizations detect emerging threats early, strengthen security, and prevent cyber attacks before they impact business

Top 10 EDR & XDR Solution Providers in India (2026): Compare Endpoint Detection & Response Platforms
Compare the top 10 EDR & XDR solution providers in India for 2026. Explore leading endpoint security platforms, features, benefits,

VAPT for Compliance: How Security Testing Helps Meet ISO 27001, PCI DSS, RBI, CERT-In & DPDP Requirements
Strengthen compliance with ISO 27001, PCI DSS, RBI, CERT-In & DPDP through VAPT. Identify security gaps, reduce risks & meet

Top 5 Cyber Crimes Targeting India’s BFSI Sector in 2026 (And How to Prevent Them)
Discover the top 5 cyber crimes targeting India’s BFSI sector in 2026 and learn effective strategies to prevent fraud, ransomware,

Top 10 Anti-Phishing & Anti-Rogue Solutions Providers in India (2026): Compare Brand Protection, Email Security & Threat Detection Services
Discover the top 10 anti-phishing and anti-rogue solution providers in India (2026). Compare brand protection, email security, and threat detection

Managed SOC Services in India (2026): Complete Enterprise Buyer’s Guide to Choosing the Right SOC Provider
Managed SOC Services in India (2026): Compare providers, features, pricing, benefits, and key factors to choose the right SOC partner

Top 10 Digital Forensics & Incident Response (DFIR) Companies in India (2026): Compare DFIR Services, Expertise & Response Capabilities
Top 10 Digital Forensics & Incident Response (DFIR) companies in India (2026). Compare DFIR services, expertise, technologies, and incident response

How to Evaluate a VAPT Report: A Practical Guide for CTOs, CISOs & IT Managers
How to evaluate a VAPT report effectively. Learn how CTOs, CISOs and IT managers can assess vulnerabilities, risks, findings and

Cyber Threat Intelligence: How Modern CTI Tools Prevent Data Breaches Faster
Discover how modern Cyber Threat Intelligence (CTI) tools detect threats early, prevent data breaches faster, and strengthen enterprise cybersecurity defenses.

Mobile Data Recovery Services: How to Recover Deleted Photos, Videos & WhatsApp Chats Fast
Recover deleted photos, videos & WhatsApp chats with expert mobile data recovery services. Fast, secure recovery for Android & iPhone

Anti Phishing Solutions: How Businesses Can Prevent Phishing Attacks in 2026
Protect your business with advanced anti phishing solutions. Learn how to prevent phishing attacks in 2026 using AI, email security,

Choosing the Right OSINT Deployment Model: On-Premise, Secured Private Cloud, or Pay-As-You-Go?
Compare on-premise, secured private cloud, and pay-as-you-go OSINT deployment models. Choose the right solution for security, scalability, and cost.

Web Application VAPT Guide: OWASP Top 10 Testing Methodology for Secure Applications
Learn the Web Application VAPT Guide with OWASP Top 10 testing methodology to identify vulnerabilities, secure web applications, and reduce

How OSINT Works: The Complete Open-Source Intelligence Process from Data Collection to Actionable Insights
Learn how OSINT works, from data collection and analysis to actionable insights. Explore the complete open-source intelligence process and its

Top 10 Most Trusted Digital Forensics Companies in India (2026) – Best Investigation Services & Forensics Solutions
Discover the top 10 most trusted digital forensics companies in India (2026). Compare investigation services, cyber forensics expertise, and incident

API Security Testing Checklist: Complete API Penetration Testing Guide for Secure APIs
Secure your APIs with our complete API Security Testing Checklist. Learn API penetration testing steps, common risks, OWASP API Top

VAPT Testing Compliance Guide: PCI DSS, RBI, ISO 27001 & SOC 2 Requirements
Understand VAPT testing compliance for PCI DSS, RBI, ISO 27001 & SOC 2. Learn requirements, benefits and how VAPT helps

How AI-Powered Cyber Attacks Are Targeting Indian Businesses in 2026
Learn how AI-powered cyber attacks are targeting Indian businesses in 2026. Explore emerging threats, real examples, and proven cybersecurity strategies.

Top 10 Most Trusted Cyber Security Companies in India (2026) – Best Cyber Security Services & Solutions Providers
Discover the top 10 most trusted cyber security companies in India (2026). Compare leading cyber security services, solutions, expertise &

Cyber Intelligence Solutions for Businesses: Tools, Features & Benefits
Discover cyber intelligence solutions for businesses. Explore top tools, key features, benefits, and how threat intelligence strengthens cybersecurity and risk

Why VAPT Testing Is Essential for Cyber Security Compliance & Business Protection
Ensure cyber security compliance with VAPT testing. Identify vulnerabilities, reduce risks, protect business data, and meet regulatory requirements.

Recent Cyber Attacks in India (2025–2026): Major Breaches Every Business Should Know
Recent cyber attacks in India (2025–2026): Explore major data breaches, ransomware incidents, and key cybersecurity lessons every business should know.

Top 10 Most Trusted VAPT Companies in India (2026) – Compare Services, Costs & Security Expertise
Discover the top 10 trusted VAPT companies in India (2026). Compare services, pricing, expertise, certifications, and choose the best cybersecurity

Best Cyber Security Company in India: Services, Solutions & Pricing Guide
Discover the best cyber security company in India. Explore top services, security solutions, pricing, and expert protection for your business.

Managed Detection and Response (MDR): A Complete Guide to Modern Threat Protection
Managed Detection and Response (MDR) provides 24/7 threat monitoring, detection, investigation, and response to stop cyberattacks before they impact.

Digital Forensics Tools: The Ultimate Guide (2026)
Explore the ultimate 2026 guide to digital forensics tools. Compare top solutions, key features, use cases, and best practices for

VAPT Testing Cost: Pricing Guide for Web, API & Cloud Security Assessments
VAPT testing cost explained: compare pricing for web, API, and cloud security assessments. Learn key factors, pricing models, and budgeting

OSINT Framework: How to Use Open Source Intelligence for Threat Detection & Investigations
OSINT Framework guide for threat detection and investigations. Learn how to gather, analyze, and leverage open-source intelligence to uncover risks.

Email Security Services: Key Features, Top Providers, Phishing Protection, and Best Practices
Discover email security services, top providers, phishing protection tools, key features, and best practices to safeguard business communications.

Top Benefits of SOC in Cyber Security for Businesses in 2026
Top benefits of SOC in cyber security for businesses in 2026: real-time threat detection, faster incident response, compliance support, and

DFIR Services: Benefits, Challenges, Tools and Future Trends
DFIR services help organizations detect, investigate and respond to cyber threats. Explore key benefits, challenges, tools and future DFIR trends.

VAPT in Cybersecurity: Audit Types, Methodology and Benefits
Learn VAPT in cybersecurity, including audit types, testing methodology and key benefits for identifying vulnerabilities and strengthening security.

Essential Cyber Security Products for Small Businesses
Protect your small business with essential cybersecurity products. Discover top tools for threat detection, data security, backups, and compliance.

Top Digital Forensics Services in 2026
Top Digital Forensics Services in 2026: Discover leading providers offering cyber investigations, incident response, data recovery, and forensic expertise.

Cyber Threat Intelligence (CTI): What It Is, Types, Lifecycle, Key Components, and Why It Matters
Learn what Cyber Threat Intelligence is, its types, lifecycle, key components, and why it matters for stronger cybersecurity decisions.

How Often Should You Perform VAPT? A Complete Guide for Businesses
Learn how often businesses should perform VAPT, what affects testing frequency, and how regular assessments help reduce cyber risks and

Top Anti-Phishing Tools and Techniques for Businesses in 2026
Protect your business in 2026 with top anti-phishing tools, AI-driven email security, employee training, and advanced threat detection techniques.

How Cybersecurity Experts Protect Businesses: Services, Strategies, and Best Practices
Learn how cybersecurity experts protect businesses with advanced services, proven strategies, and best practices to prevent cyber threats and data

VAPT Services: Types of Penetration Testing, and Key Benefits
Strengthen security with VAPT services, including network, web, and mobile penetration testing to identify vulnerabilities and reduce cyber risks.

Top Cyber Security Services to Watch in 2026
Explore the top cyber security services to watch in 2026, from AI-driven threat detection to cloud security and zero trust

Types of Digital Forensics Products Every Investigator Should Know
Explore essential digital forensics products investigators use, from disk imaging and mobile analysis to network, cloud, and malware forensics tools.

How MDR Services Provide 24/7 Threat Detection & Rapid Incident Response
24/7 MDR services deliver real-time threat detection, rapid incident response, and expert security monitoring to stop cyberattacks before damage occurs.

Why Indian Businesses Need Advanced Anti-Phishing and Anti-Rogue Solutions in 2026
Why Indian businesses need advanced anti-phishing and anti-rogue solutions in 2026 to prevent fraud, secure brands, protect customers, and ensure

VAPT: Vulnerability Assessment and Penetration Testing (Types)
Explore types of VAPT—Vulnerability Assessment and Penetration Testing—to identify, assess, and secure systems against evolving cyber threats effectively.

What Are Cyber Intelligence Solutions and Why Do Government Agencies Need Them?
Discover why Cyber Intelligence Solutions are vital for government agencies to detect threats, enhance security, and protect national infrastructure.

Vulnerability Scanning Price in India: Complete Cost Breakdown for 2026
Discover vulnerability scanning costs in India for 2026, detailed pricing, factors, tools, and service comparisons to help you choose the

How to Choose the Right DFIR Services Provider in India
Find the best DFIR services provider in India with expert tips on experience, tools, response time, and compliance to protect

How a SOC Network Protects Your Business from Advanced Cyber Threats
Protect your business from advanced cyber threats with a SOC network real-time monitoring, rapid response, and proactive security to keep

Common Security Risks in Indian Businesses & How VAPT Services Prevent Cyber Attacks
Protect your business from cyber threats. Discover common security risks in Indian companies and how VAPT services help prevent attacks

How Managed Detection & Response Services Work: Functions, Pros, and Business Value
Learn how Managed Detection & Response (MDR) services work, including key functions, benefits, and the business value they deliver for

How Anti-Phishing & Anti-Rogue Services Work to Stop Modern Cyber Threats
Learn how Anti-Phishing and Anti-Rogue security services detect, block, and eliminate fake websites, scams, and malware to protect users from

Why Digital Forensics and Incident Response Is Critical for Modern Cybersecurity
Digital Forensics and Incident Response (DFIR) help organizations detect, investigate, and recover from cyberattacks, strengthening modern cybersecurity defenses.

Core Components of VAPT: Services, Process, and Security Advantages
Core components of VAPT explained services, step-by-step process, and key security advantages to strengthen cybersecurity and protect your business from

Why Every Organization Needs VAPT Solutions to Prevent Data Breaches
Why every organization needs VAPT solutions to prevent data breaches, strengthen cybersecurity, reduce risks, and protect sensitive business data.

How to Choose the Right VPS Hosting Service: Benefits, Types, and Provider Strengths
Choose the right VPS hosting service with our guide on benefits, VPS types, and provider strengths to ensure performance, scalability,

Best SOC Service Providers in India: Features, Models, and SOCaaS Options
Explore top SOC service providers in India, key features, delivery models, and SOCaaS options to strengthen your cybersecurity strategy.

Types of Cloud Services: Features, Benefits, and Top Cloud Providers
Explore types of cloud services IaaS, PaaS, SaaS their features, benefits, and top providers to choose the right cloud solution

How Managed Detection and Response Services Help Businesses Minimize Cybersecurity Risks
Managed Detection and Response services help businesses reduce cybersecurity risks with 24/7 monitoring, threat detection, rapid response, and expert security

The Role of DFIR in Cybersecurity Investigations and Threat Mitigation
DFIR in Cybersecurity Investigations helps detect breaches, analyze digital evidence, and mitigate cyber threats to strengthen organizational security and resilience.

Cloud VPS Hosting Services: How They’re Powering Scalable & Secure Websites in 2026
Cloud VPS hosting in 2026 delivers scalable, secure, high-performance infrastructure that helps websites grow faster, stay protected, and handle traffic

How VAPT Solutions Help Organizations Prevent Cyber Attacks in 2026
Learn how VAPT solutions in 2026 help organizations identify vulnerabilities, strengthen security posture, and proactively prevent advanced cyber attacks.

How to Choose the Best Colocation Hosting Provider in India
Learn how to choose the best colocation hosting provider in India by evaluating security, uptime, connectivity, scalability, and cost efficiency.

SOC Services: Ultimate Guide to Choosing the Best SOC Solutions Provider
Learn how to choose the best SOC services provider. Compare SOC solutions, features, pricing, and benefits with expert guidance and

Top 7 Cloud Services & Solutions Every Business Needs in India (2026 Guide)
Discover the top 7 cloud services and solutions every business in India needs in 2026 to boost scalability, security, efficiency,

How to Choose the Best Managed Data Center Service Provider in India (2026 Checklist)
Learn how to choose the best managed data center service provider in India with this 2026 checklist covering security, compliance,

Ultimate Guide to VAPT Services & Pricing in India (2026)
Comprehensive 2026 guide to VAPT services in India—types, methodology, compliance requirements, pricing models, and how to choose the right provider.

SOC-as-a-Service Pricing: Understanding Costs, Models & Strategic Value
Explore SOC-as-a-Service pricing—cost drivers, pricing models, and strategic value—to choose the right SOC solution without overspending.

Dedicated Server Hosting: Why It’s Still the Right Choice for Performance-Driven Businesses
Discover why dedicated server hosting remains the best choice for performance-driven businesses needing speed, security, reliability, and full control.

VAPT Audits: A Complete Guide to Methods, Pricing & Security Advantages
Comprehensive guide to VAPT audits covering methods, costs, pricing models, and key security benefits to protect systems from vulnerabilities.

How Managed Service Providers (MSPs) Drive Business Efficiency Through Automation & IT Modernization
Managed Service Providers boost efficiency through automation and IT modernization, reducing costs, improving security, and enabling scalable business growth.

Anti-Phishing Solutions: Effectiveness, Limitations & What Really Keeps You Safe
Explore anti-phishing solutions—their effectiveness, limitations, and what truly keeps you safe from phishing attacks in today’s evolving threat landscape.

How VPS Hosting Enhances Website Speed, Security, and Scalability
VPS hosting boosts website speed, strengthens security, and enables easy scalability—delivering better performance, control, and reliability for growing sites.

A Beginner’s Guide to Cybersecurity Managed Services: Benefits, Features & Trends
Beginner’s guide to cybersecurity managed services covering benefits, key features, use cases, and latest trends to protect businesses from threats.

How to Select the Best VAPT Service Provider: Essential Criteria for Modern Businesses
Learn how to choose the best VAPT service provider with key criteria like expertise, tools, compliance, reporting quality, and post-test

How Next-Generation Networks Are Driving Demand for High-Performance Colocation Infrastructure
Learn how next-generation networks like 5G and edge computing are driving demand for Colocation Infrastructure to deliver low latency and

What Is EDR in Cyber Security? Overview, Benefits & Core Capabilities
Learn what EDR in cybersecurity is, how it works, its benefits, core capabilities, and top tools in 2026 to protect

SOC as a Service (SOCaaS): A Smarter Way to Secure Your Business in 2026
Discover why SOC as a Service is the smarter security choice for 2025. Explore benefits, pricing, features, and how SOCaaS

Top Cybersecurity Threats Indian Enterprises Face in 2026
Indian enterprises in 2026 face major Cybersecurity Threats, from AI-driven attacks to data breaches. Learn key risks and ways to

Top 10 Benefits of Cloud Managed Services for Businesses
Cloud Managed Services boost performance, reduce IT costs, and support growth. Discover the top 10 benefits of cloud managed services

DPDP Act & Forensic Readiness: Compliance, Penalties, and Key Trends to Watch in 2026
Explore DPDP Act compliance, forensic readiness essentials, penalties, and 2026 trends shaping data protection and investigative resilience.

ECSplorator: The Next-Gen Forensic Workstation and High-Performance Server Solution
ECSplorator delivers a cutting-edge forensic workstation and high-performance server solution designed for rapid analysis, secure data handling, and unmatched efficiency.

Vulnerability Assessment & Penetration Testing (VAPT): Strengthening Your Cybersecurity Defense in 2026
Discover how Vulnerability Assessment and Penetration Testing (VAPT) can fortify your cybersecurity defense in 2026. Learn its benefits, types, and

Why Dedicated Server Hosting Is the Powerhouse behind High-Performance Websites and Growing Businesses
Dedicated Server Hosting delivers high performance, security, and scalability. Discover its benefits and why it powers growing businesses and websites.

Comprehensive Guide to VAPT Services in India: Why Expert Consulting and Auditing Matter
Discover top VAPT Services in India with expert consulting and auditing. Ensure your business’s cybersecurity through comprehensive vulnerability testing.

Mobile App VAPT: What You Need to Know to Keep Your Apps Safe from Unknown Threats
Stay ahead of cyber threats with Mobile App VAPT. Learn how vulnerability assessment and penetration testing keep your mobile apps

VPS Hosting Services Explained: The Ultimate Guide to High Performance, Security, and Scalable Growth
VPS Hosting Services improve speed, security, and scalability. Discover why VPS hosting services are ideal for growing websites and online

How ECS Strengthens Business Security with Managed Cybersecurity Services?
Stay secure in the digital era with ECS’s managed cybersecurity services. Explore how ECS delivers end-to-end protection, compliance support, and

Why Data Center Colocation Is the Key to Building a Reliable, Scalable, and Cost-Efficient IT Infrastructure
Data Center Colocation boosts reliability, scalability, and cost-efficiency. Discover why businesses choose it for modern, high-performance IT infrastructure.

How Much Does Penetration Testing Cost in 2025? A Complete Pricing Guide
Find out how much penetration testing costs in 2025, from pricing in India to global rates, and learn what impacts

Dedicated Server Hosting: The Ultimate Guide for High-Performance Websites
Dedicated Server Hosting offers unmatched speed, control, and security for high-traffic sites and enterprise apps. Learn why it’s the ultimate

Everything You Need to Know About VPS Hosting for Modern Businesses
Discover how VPS hosting empowers modern businesses with speed, security, and scalability. Learn why it’s the perfect upgrade from shared

Cyber Security Solutions: How to Protect Your Business & Enterprise Networks in 2025
Safeguard your enterprise with next-gen cyber security solutions. Explore types, benefits, and how to choose the right protection for your

Top Reasons Businesses Choose Colocation Services for Growth and Security
Discover how Colocation Services enhance growth, security, and reliability. Learn why businesses choose them for flexible, scalable IT infrastructure.

Staying Ahead of Cyber Adversaries: A Deep Dive into Cyber Threat Intelligence Solutions & Services
Stay ahead of cyber adversaries with Cyber Threat Intelligence solutions, services, and best practices to protect your business from evolving

Uncovering Digital Truths: The Ultimate Guide to Digital & Cyber Forensics Services in India
Stay ahead of cyber threats with digital forensic services in India. From data recovery to court-admissible evidence, discover why trusted

Network Penetration Testing: The Complete Guide to Network Security Testing & Cost Insights
Strengthen your defences with this complete guide to network security testing, including phases, tools, costs, and remediation strategies.

Web Application VAPT: The Essential Guide to Web Application Security Testing & Penetration Testing
Strengthen your web apps with VAPT. Our essential guide covers testing methods, benefits, and best practices in penetration testing.

Top Cyber Security Company in Ahmedabad | Why ECS Leads in Cybersecurity Solutions
ECS is the top cyber security company in Ahmedabad, offering advanced cybersecurity solutions, threat protection & compliance for businesses.

Insider Threat Detection: 7 Indicators You Can’t Ignore
Insider threats can cost businesses millions. Discover 7 key indicators of insider threat detection you can’t ignore to protect your

Why Do You Need VAPT? Top Reasons Every Business Must Prioritize Security Testing in 2026
Learn why VAPT is crucial in 2026. Identify vulnerabilities, prevent cyber threats, and protect your business with effective security testing

Insider Investigation Service: Safeguarding Your Business with Effective Insider Threat Detection
Safeguard your business with our Insider Investigation Service. Detect, prevent, and manage insider threats with expert detection and protection solutions.

How to Choose the Right VPS Hosting Service for Your Business in 2026?
Discover how to choose the best VPS hosting in 2026. Compare features, performance, and pricing to find the right VPS

Vulnerability Assessment & Penetration Testing: Key Differences and How VAPT Services Protect Your Business
Discover the key differences between vulnerability assessment & penetration testing, and how VAPT services strengthen security to protect your business.

How to Secure Your VPS: A Step-by-Step Guide
Learn how to secure your VPS with this step-by-step guide. Protect your server from threats using best practices for safety,

Insider Threat Detection Tools: Key Requirements, Challenges, and Complete Solutions
Insider threat detection tools: explore key requirements, challenges, and complete solutions to protect organizations from internal security risks.

The Ultimate Guide to Network Forensics in India: Importance, Tools, and Real-World Applications
Discover network forensics in India: its importance, key tools, and real-world uses to combat cybercrime and enhance digital security.

The Future of VAPT Services: Automation and Evolving Threats in 2026
Explore VAPT Services in 2026 using automation to tackle evolving threats, enhance security efficiency, and strengthen business resilience.

What Are Insider Threats? Types, Real Examples, Risks, and Prevention Strategies
Insider threats are security risks from within an organization. Learn types, real examples, risks, and prevention strategies to protect your

Shared Hosting vs. VPS Hosting in 2026: What’s Best for Your Website?
Compare Shared Hosting vs. VPS Hosting in 2026. Learn performance, security, and cost differences to choose the best option for

Cyber Attack Prevention Guide 2026: 7 Proven Strategies from Top Cybersecurity Experts
Follow this Cyber Attack Prevention Guide with 7 proven strategies to protect your business, reduce risks, and stay ahead of

Data Center Services: Powering Secure, Scalable Business IT Infrastructure
Explore Data Center Services to boost security, uptime, and scalability. Build reliable IT infrastructure and protect your business with advanced

Cloud Managed Services: Optimize, Secure & Scale Your Business in the Cloud
Boost efficiency with Cloud Managed Services. Optimize performance, enhance security, and scale your business with reliable, expert cloud solutions.

Mobile App VAPT: A Complete Guide to Mobile Application Penetration Testing
Learn Mobile App VAPT to identify vulnerabilities, apply best practices, and secure mobile apps with effective penetration testing techniques.

VAPT Testing Explained: Why Your Business Needs It for Cyber Defense
Learn VAPT Testing to uncover vulnerabilities, prevent cyber threats, and strengthen your business security with expert cyber defense strategies.

Unlocking Evidence: ECS Infotech’s Expert Mobile Forensics Services
Unlock digital evidence with ECS Infotech’s expert mobile forensics services. Reliable data recovery, analysis & legal support for investigations.

Rescue, Restore, Recover: The Complete Guide to Data Recovery Services in Ahmedabad & India
Discover top data recovery services in Ahmedabad & across India. Learn how experts rescue, restore & recover your lost data

Top Cybersecurity Solutions Every Business Needs in a Digital-First World
Discover Cybersecurity Solutions to protect data, prevent threats, and secure your business in today’s fast-evolving digital-first world.

Inside the Ledger: A Comprehensive Guide to Blockchain & Cryptocurrency Investigation Solutions
Explore blockchain & cryptocurrency investigation tools, techniques, and solutions in this in-depth guide for tracking, analyzing, and securing digital assets.

A Comprehensive Guide to Vulnerability Assessment & Penetration Testing (VAPT Services) in India
Learn Vulnerability Assessment & Penetration Testing to identify risks, tools, and processes. Strengthen security with VAPT services in India effectively.

Exploring the Scope of Digital Forensics Services
Discover the wide scope of digital forensics services, including data recovery, cybercrime investigation, and legal support for digital evidence analysis.

Empowering Deepcall India Pvt. Ltd. with Reliable Colocation Data Center Services
Boost uptime with Colocation Data Center Services. Secure, scalable solutions empower Deepcall India Pvt. Ltd. with reliable and efficient IT

Chip‑Off Forensics in India: The Definitive Guide to Advanced Chip‑Off Digital Forensics & Data Recovery
Discover the ultimate guide to Chip-Off Forensics in India. Learn advanced techniques for digital forensics, data recovery & mobile chip-level

Cyber Security Solutions: How ECS Protects Your Business with Expert Cyber Security Management & Services
Explore Cyber Security Solutions by ECS for threat protection, risk management, and 24/7 monitoring to keep your business secure from

Everything You Need to Know About Data Recovery Services: Protect, Recover & Restore Your Critical Data
Need to recover lost files? Learn the step-by-step data recovery process, industry best practices, and how professionals restore critical business

Cryptocurrency and Fraud Investigations: Uncovering Digital Trails in the Crypto Era
Discover effective crypto investigations solutions and best practices to trace and prevent digital fraud in the blockchain and cryptocurrency era.

Hosting Confidence: A Fintech Leader’s Shift to ECS Data Center Services in India
Discover how Data Center Services in India helped a fintech firm boost performance, security, and scalability with ECS solutions.

Mastering Web Application Penetration Testing: A Complete Guide
Master Web Application Penetration Testing to find flaws, fix vulnerabilities, and secure apps and infrastructure from cyber threats effectively.

Chip-Off Forensics Services: Unlocking Critical Data from Damaged Devices
Expert Chip-Off Forensics services to recover vital data from damaged or locked devices. Trust our specialists for secure, reliable digital

A Complete Guide to Network Penetration Testing for Business Security
Learn Network Penetration Testing to detect vulnerabilities, strengthen defenses, and secure your business with this complete, practical guide.

VAPT Testing: How a Financial Firm Closed Critical Security Gaps with ECS
See how VAPT Testing helped a financial firm fix critical flaws, strengthen cyber defenses, and achieve compliance with ECS security

Email Security Solutions: How to Prevent Phishing and Cyber Attacks
Learn what email security is, why it’s essential, and discover best practices to protect your business from phishing, spam, and

Colocation Solutions: Secure, High-Density & High-Performance Data Center Hosting
Explore secure colocation solutions for enterprise, high-density and HPC workloads, with high bandwidth, data center security, backup and scalable infrastructure.

Mobile Application VAPT: Complete Guide to Mobile App Security Testing
Learn how mobile application VAPT identifies security vulnerabilities in Android and iOS apps through vulnerability assessment, penetration testing and security

How ECS Delivered Scalable Data Center Services for a Growing Startup
Discover how ECS Infotech delivered scalable data center services to help a growing startup build reliable, secure and business-ready IT

Network Penetration Testing: Process, Methodology, Benefits & Cost
Learn how network penetration testing identifies security weaknesses through scanning, vulnerability assessment and controlled testing, including methodology, benefits and cost.

VAPT Services for an Industrial Packaging Manufacturer: Cybersecurity Case Study
Explore how ECS Infotech delivered VAPT services for an industrial packaging manufacturer to identify security vulnerabilities and strengthen its cybersecurity

Top Anti-Phishing Strategies to Protect Your Business in 2025
Discover the top anti-phishing strategies for 2025 to protect your business from cyber threats. Learn how to detect, prevent, and

Managed Dedicated Hosting: Benefits, Features & Services
Explore managed dedicated hosting benefits, features and services, including server management, security, monitoring, performance and technical support.

Managed Colocation Hosting for a Growing EdTech Platform
Discover how ECS delivered scalable managed colocation hosting for a leading EdTech platform, supporting performance, reliability, security and business growth.

Web Application Penetration Testing & VAPT Services
Protect web applications with expert VAPT and penetration testing services in India. Identify vulnerabilities, validate security risks and strengthen application

SOC for Fintech Companies: How ECS Strengthened Security Operations
See how ECS delivered SOC services for a growing fintech company to strengthen security monitoring, threat detection, incident response and

VAPT: Complete Guide to Vulnerability Assessment and Penetration Testing
Learn what VAPT means, how vulnerability assessment and penetration testing work, VAPT types, process, tools, benefits, costs, reports and security
Data Recovery Services: Restoring Lost Data with Cutting-Edge Solutions
Recover lost data with advanced data recovery services. Get expert solutions for accidental deletion, hardware failure, or cyber threats. Restore
Anti-Phishing and Anti-Rogue Solutions: Safeguarding Your Business from Digital Threats
Protect your business from cyber threats with advanced anti-phishing and anti-rogue solutions. Stay secure with real-time monitoring and threat mitigation.
Digital Forensics Services: Uncovering the Truth in Cyber Investigations
Learn about types, processes, and future trends in digital forensics - essential for solving cyber investigations and securing data.

VAPT Audit: Complete Guide to Process, Checklist, Report & Compliance
Learn what a VAPT audit is, how the audit process works, what a VAPT report and checklist include, key compliance

Vulnerability Assessment: Benefits, Process, Tools & Complete Guide
Learn what vulnerability assessment is, its benefits, process, tools and cost. Discover how vulnerability scanning identifies security weaknesses and supports
How to Protect Your Business from Phishing Attacks – Essential Tips & Strategies
Learn how to protect your business from phishing attacks with essential tips and strategies to prevent data breaches and enhance

Future of Professional Data Recovery Services: Predictions & Emerging Trends for 2025
Explore the future of professional data recovery services with key predictions and emerging trends for 2025, ensuring data security and

VAPT Testing: Complete Guide to Services, Process, Cost & Security
Learn what VAPT testing is, how vulnerability assessment and penetration testing work, what VAPT services cover, how much testing can

ECS Narnarayan Shastri Institute of Technology (NSIT) Sign MoU to Strengthen Cybersecurity Education
ECS and NSIT sign MoU to advance cybersecurity education. Strengthening skills, innovation, and industry-ready talent for a secure digital future.

Virtual Private Server Hosting: Complete Guide to VPS Solutions for Businesses
Explore virtual private server hosting for businesses with secure, scalable and reliable infrastructure. Learn VPS benefits, features, use cases, management

How Digital Evidence Specialists Protect Banks from Hidden Risks
Discover how digital evidence specialists help banks uncover hidden risks, prevent fraud, and strengthen cybersecurity with advanced forensic techniques.

Server Colocation Services: Managed Data Center Solutions for Businesses
Explore server colocation services for secure, reliable and scalable IT infrastructure. Learn how managed colocation data centers support server security,

Anti-Phishing Solutions: How to Safeguard Your Business from Cyber Threats
Protect your business from cyber threats with advanced anti-phishing solutions. Learn how to detect, prevent, and mitigate phishing attacks effectively.

Web Application VAPT: Complete Guide to Security Testing and Penetration Testing
Learn how web application VAPT identifies vulnerabilities, security risks and attack paths. Explore the testing process, techniques, reporting, ISO 27001

Colocation Data Centers: The Smart Choice for Scalable, Secure, and AI-Driven Infrastructure
Discover how Colocation Data Centers power scalable, secure, AI-driven infrastructure. Learn why businesses choose them for reliable IT performance.

Building a Future-Ready CSOC: Balancing People, Technology, and Security
TABLE OF CONTENTS The Evolution of Security Operations Centers Why Cyber Security Operation Centers Are More Critical Than Ever Technology
Protecting Your Inbox: The Role of Email Security Companies and Solutions
Introduction An estimated that cybercriminals send 3.4 billion potentially malicious emails daily, which through forgery masquerade as messages from familiar

SAST vs. DAST: Choosing the Right Approach for Application Security with VAPT Companies in India
Learn SAST vs. DAST differences to choose the right app security approach. Discover how VAPT companies in India use both
Cyber Threat Intelligence Solutions: A Roadmap to Proactive Security
Introduction Cyber threats are evolving faster than ever before, demanding the shift from traditional midway reactive security towards intelligence-driven proactive tactics.
Insider Threat Cybersecurity: Addressing the Risks of Departing Employees and Data Theft
The modern digital world still overlooks insider threats as one of the most underappreciated cybersecurity dangers. Internal security risks become
How Cyber Security Solutions and Forensic Expertise Shielded Against 2024’s Worst Attacks
Cyber threat level went through new highs in 2024 and organizations became at risk of sophisticated and specialized attacks. Cybercrime

Why Transparency Sets the Best VAPT Companies in India Apart
Learn how the Best VAPT Companies in India stand out through transparency, delivering clear insights, reliable testing, and stronger cybersecurity
How Digital Forensics Solved High-Profile Data Breach Cases
Discover how Digital Forensics experts solved high-profile data breach cases by uncovering evidence, tracing hackers, and restoring compromised data.
Crisis Management Made Easy: Unlocking the Power of Case Management Services and Specialists
In the current world, organizations encounter different crises, including cyber threats, legal issues, health crises, and others. Managing these challenges

Garuda Advertisement’s Digital Leap: Best Virtual Private Server Solution Delivered Seamlessly
Discover how a Virtual Private Server Solution enabled Garuda Advertisement’s digital leap with enhanced performance, scalability, and reliability.
Unheard and Unseen: The Ethical Dilemmas of Forensic Audio-Video Analysis
TABLE OF CONTENTS Understanding Forensic Audio-Video Analysis Conclusion In today’s society where technology is advancing at an alarming rate, forensic
Cross-Border Investigations: The Role of Forensic Cell Phone Data Recovery in 2025
Introduction In an increasingly interconnected world, the scope of criminal investigations transcends national borders. With mobile devices being an integral

Cloud Forensics: Investigating the New Frontier of Cybersecurity
Introduction Cloud forensics has become an overstated issue due to the growing popularity of cloud computing in many businesses to

The Relationship of Network Forensics and Analysing Dark Web Traffic
The hidden web that is only available through the means of accessing the TOR browser is well established in criminal
Multimedia Forensics: Protecting Integrity in the Era of Digital Manipulation
With advancements in technology, digital content is readily available everywhere, it is essential to protect the integrity of audio-visual evidence.

Understanding Black Box, Gray Box, and Red Teaming Cybersecurity Services
Explore Cybersecurity Services including Black Box, Gray Box, and Red Teaming to strengthen defenses, identify risks, and improve security posture.

Forensics in the Metaverse: The Next Frontier for Digital Forensics Specialists
The metaverse, a virtual world blending augmented reality (AR), virtual reality (VR), and blockchain technologies, is fast becoming a space
Exploring the Latest Innovations in Data Recovery Services and Forensic Disk Recovery
In today’s digital era, data is one of the most valuable assets for individuals and organizations alike. Losing access to

The Role of VPS in Scaling Online Businesses in 2026
Explore the Role of VPS in scaling online businesses in 2026 with better performance, flexibility, security, and cost-effective hosting solutions.

Unlocking the Truth: The Role of Cell Phone Forensics Services in Modern Investigation
In an era dominated by mobile communication and digital footprints, cell phone forensics services and the expertise of digital forensics

The Evolution of SOC-as-a-Service: What SMBs Need to Know
Cybersecurity is no longer a concern exclusive to large enterprises. With the increasing frequency and sophistication of cyber threats, small

The Role of Disk Forensics in Modern Cybersecurity: Tackling Insider Threats
As organizations increasingly rely on digital infrastructure, insider threats have become one of the most challenging cybersecurity risks. These threats,
Cloud Forensics: Navigating Challenges and Embracing Innovations
The rapid adoption of cloud technologies has revolutionized how businesses operate, but it has also introduced a new dimension to
Phishing Protection 101: How Anti-Phishing Solutions Can Save Your Business from Fraud
Introduction Phishing attacks are one of the most prevalent threats, and fraudsters perpetually evolve their strategies to gather sensitive information

Colocation Data Center Solution for Leading Automobile Distributor
Discover how a Colocation Data Center Solution boosts performance, security, and scalability for leading automobile distributors with reliable infrastructure.
Strengthening Digital Defenses: How Cyber Investigation and Cyber Security Solutions Combat Evolving Threats
Introduction In today’s digital-first economy, cyber threats are at an all-time high. According to recent reports, global cybercrime costs are
Strengthening Your Cyber Defenses: Modern Email Security Solutions and Forensic Email Recovery
In today’s digital landscape, email remains a primary channel for communication—and, unfortunately, for cyber-attacks. With phishing, malware, and sophisticated social

Navigating Financial Fraud: The Latest Strategies for Effective Recovery and Investigation
Explore the latest strategies to combat Financial Fraud, enhance recovery efforts, and strengthen investigations for better financial security and protection.

Strengthening Bank Security with ECS – A Leading Cyber SOC Service Provider in India
Discover how a Cyber SOC Service Provider in India like ECS strengthens bank security with 24/7 monitoring, rapid response, and

Stay Ahead of the Hackers: 6 Must-Know Security Lessons for Cybersecurity Awareness Month and Beyond
Learn essential tips this Cybersecurity Awareness Month to stay ahead of hackers with 6 key lessons on protecting data, systems,

Digital Forensics Solutions for Corporate Data Leaks on Social Media Platforms
Discover effective Digital Forensics Solutions to investigate and prevent corporate data leaks on social media platforms with advanced forensic tools.

Implementing a Comprehensive Network Access Control (NAC) Solution for a Leading Clinical Research Organization
Discover how a Network Access Control Solution strengthens security with device control, access policies, and real-time monitoring for enterprises.

Forensic Mobile Phone Data Recovery: Techniques, Tools & Evidence Extraction
Learn forensic mobile phone data recovery techniques, including mobile data extraction, deleted evidence recovery, Android forensics, tools and analysis.

Understanding Data: A Foundation for Digital Forensics Data Recovery
Data refers to any information that holds value for a user, which could be in the form of emails, text

Don’t Fall for It: The Ultimate Guide to Protecting Yourself from Social Engineering Attacks
Learn how to prevent Social Engineering Attacks with expert tips, awareness strategies, and security practices to safeguard your data and
Behind the Inbox: The Power of Email Forensics in Cyber Defense
Email is still one of the key ways that people and businesses communicate in today’s digital world. It is also

Exploring Cloud Data Centers: A Comprehensive Guide by Leading Dedicated Server Hosting Solution Provider in Gujarat
Explore Cloud Data Centers in this comprehensive guide, covering benefits, scalability, and secure hosting solutions for modern businesses in Gujarat.
Unveiling the Digital Detectives: Computer Forensic Analyst vs. Consultant Explained
Cybercrime has become one of the biggest problems facing law enforcement, corporations, and individuals in today’s technologically advanced world. The

Forensic Analysis of Zero-Day Exploits: Advanced Techniques in Network Forensics
Introduction Zero-day threats are some of the most hostile threats that cyber criminals can unleash in today’s world. These attacks

Strengthening Brand Reputation and Ensuring RBI Compliance for a Leading Fintech Corporate
Learn how RBI Compliance helps fintechs strengthen brand reputation, meet regulatory standards, and enhance trust with secure, compliant operations.
The Future of Digital Forensics in the Cloud: Navigating Challenges and Embracing Innovations
Discover how Digital Forensics is evolving in the cloud era. Learn to navigate challenges, embrace innovations, and enhance cybersecurity investigations.

The Critical Intersection of Cyber Threat Intelligence and Insider Threat Protection
Learn how Cyber Threat Intelligence strengthens insider threat protection by detecting risks, improving security, and preventing data breaches.

Why Legacy Firewalls and VPNs Are Not Enough: The Need for Network VAPT in Modern Cybersecurity
Learn why Network VAPT is essential beyond firewalls and VPNs, helping detect vulnerabilities, strengthen defenses, and secure modern IT environments.
Innovative Case Management Services: How ECS Infotech’s Specialists Are Shaping the Future
Over the period, there has been great concern on the subject of case management given the fact that it is

Safeguarding Modern Enterprises: Effective Data Backup and Recovery Solutions
Discover how Data Backup and Recovery Solutions protect modern enterprises with secure storage, fast recovery, and resilience against data loss
The Growing Demand for Cyber Forensic Consultants in the Era of Data Breaches
Cybersecurity threats including hackers and cyber criminals are rampant in today’s society not sparing business entities big and small and

Forensic Data Recovery: Techniques, Methods, Tools & Digital Forensics
Explore forensic data recovery techniques, methods and tools used in digital forensics to recover, examine and preserve digital evidence.

Transforming Cybersecurity for an Urban Cooperative Bank with Tailored SOC Services
Discover how SOC Services enhance cybersecurity for urban cooperative banks with real-time monitoring, threat detection, and tailored protection strategies.
The Importance of Chain of Custody in Audio and Video Forensic Analysis
Ensure evidence integrity with a proper chain of custody. Learn its vital role in preserving authenticity in audio & video

Common Scenarios Where Password Recovery Services Are Needed
Introduction Today, password acts as many people’s barrier to protect their own data and the data of the organizations they

Ransomware Attack Cripples over 300 Indian Banks: A Significant Blow to India’s Banking Infrastructure
Explore how a major Ransomware Attack impacted over 300 Indian banks, exposing vulnerabilities and highlighting urgent cybersecurity measures needed.

Unlocking Secrets: The Power of Mobile Forensics in Data Recovery
Unlock the full potential of mobile phone forensic recovery to seamlessly retrieve lost data. Dive into the power of forensic

Secure Your Data: The Power of Forensic Data Recovery Services
In today’s world people heavily rely on technology, and it becomes impossible to imagine the loss of any important information.
The Evolving Role of Cyber Forensic Consultants and Experts in Modern Cybersecurity
Cybersecurity plays great importance in the present generation where technology has advanced a lot. Correspondingly to the increase of the

The Evolution of Digital Forensics in the Cloud
Cloud computing has become an integral part of modern business infrastructure, revolutionizing how we develop applications, broker services, and store

Enhancing E-Commerce Growth with ECS Colocation Services in Gujarat
Discover how Colocation Services enhance e-commerce growth in Gujarat with scalable infrastructure, high uptime, and secure data center solutions.
Top Benefits of Implementing Case Management Services in Your Company
In the current environment, organizations are always looking for avenues to increase productivity, satisfy clients, and improve on their compliance
Unmasking Cyber Threats: The Importance of Phishing Email Forensics in Email Security
Today, when lives are entwined with technology, mailing is one of the most common methods of people’s communication. But it

In-House Expertise vs. Managed CSOC Services: Choosing the Right Security Operations Center for Your Organization
Compare In-House Expertise vs. Managed CSOC Services to choose the right SOC model, improve threat response, reduce costs, and strengthen
Unlocking the Mysteries of Cyber security: A Deep Dive into Computer and Digital Forensics
In the digital age, our lives are intricately woven with technology. From everyday communication to sophisticated business operations, everything relies

The Importance of Secure Cloud Backup Solutions for Remote Users
Discover how Secure Cloud Backup Solutions protect remote users’ data with encryption, easy recovery, and reliable access from anywhere, anytime.

Managing Cybersecurity: Being aware Threats, Vulnerabilities, and Risks
Learn how Cybersecurity helps manage threats, vulnerabilities, and risks with strategies to protect data, systems, and business operations effectively.

Social Media Forensics: Unveiling the Dark Side of Social Networks
Explore how Social Media Forensics uncovers hidden evidence, tracks cybercrimes, and exposes the dark side of online social networks.

The Critical Role of Call Detail Record Analysis and Cell Phone Forensics in Legal Matters
Discover how Cell Phone Forensics and call detail record analysis play a vital role in solving cases, uncovering evidence, and

Understanding Password Recovery vs. Password Cracking: Key Differences and Solutions
In today’s digital age, where cybersecurity is paramount, the concepts of password recovery and password cracking play pivotal roles in
The Essential Guide to Audio and Video Forensics in Digital Investigations
Discover key techniques in audio & video forensics for digital investigations. Learn tools, methods & best practices to uncover truth

What Is Colocation? How Does it Enable Modern Digital Infrastructure?
Discover how Colocation supports modern digital infrastructure with scalable, secure data center solutions that enhance performance and reliability.
Unlocking the Secrets: Forensic Mobile Phone Data Recovery & Cell Phone Forensic Services
Explore expert Cell Phone Forensic Services for secure mobile data recovery, evidence extraction, and advanced digital investigation solutions.
Advanced Techniques in Email Forensics: Enhancing Cyber Security Solutions
Discover advanced techniques in Email Forensics to strengthen cyber security solutions, detect threats, and enhance digital investigation accuracy.

How Your Digital Assets Are Secured When You Select the Correct VAPT Service Provider
Learn how a trusted VAPT Service Provider secures digital assets through vulnerability assessment, penetration testing, and proactive threat protection.

Unraveling the Riddles of Digital Cloud Forensics: A Guide on How to Go through Investigations in Cloud
In our dynamic tech world, cloud computing is an influential technology that companies have adopted globally. It has become synonymous

Managing Insider Threats: A Strategic Approach to Protecting Your Business
Introduction Threats towards businesses nowadays can take many forms, ranging from cyber-attacks to internal misconduct. Insider threats are particularly devious, posing major hazards to

Unraveling the Intricacies of Database Forensics: Safeguarding Digital Assets
Introductions In today’s digital landscape, where the threat of data breaches looms large, the importance of robust database security solutions

Navigating the Shadows: How Dark Web Monitoring Strengthens Cybersecurity
Discover how Dark Web Monitoring enhances cybersecurity by detecting threats early, protecting sensitive data, and preventing breaches in real time.
Understanding Password Recovery Solutions: Securing Access While Maintaining Convenience
Understand password recovery solutions, how they secure account access, reduce login risks, and balance strong security with user convenience for

5 Compelling Reasons to Choose Windows VPS Hosting for Your Business in Gujarat
Discover why VPS Hosting with Windows VPS is ideal for businesses in Gujarat, offering performance, security, scalability, and cost-effective solutions.

Discovering the Power of Social Media Investigations: A Deep Dive into Forensic Social Media Investigation
Explore the power of Social Media Investigations with forensic techniques that uncover digital evidence, enhance security, and reveal online insights.

Unveiling the Mysteries of Mobile Device Forensics: Insights from a Cell Phone Forensic Expert
Explore mobile device forensics with a cell phone forensic expert—discover tools, techniques, and real-world insights into digital evidence recovery.

Unlocking the Secrets of Advanced Network Forensics: A Guide by Digital Forensic Consultants
A subset of digital forensics known as “network forensics” is primarily concerned with examining networks and the traffic that passes

Boosting Cybersecurity Strength; A Case Study of Innovative Solutions for Cyber Consultants by ECS
Explore how Cyber Consultants benefit from ECS innovative solutions, enhancing cybersecurity strength, threat detection, and risk management strategies.
Understanding Insider Threats: A Critical Component of Cybersecurity
Within the field of cybersecurity, the phrase “insider threat” holds great importance. While protecting against external threats like malware and

Uncovering Financial Deception; The Vital Role of Investigation and Recovery
Dealing with fraud remains an issue that significantly impacts the trustworthiness of the banking sector posing substantial risks to both
Unveiling the Mysteries of Cloud Computing Forensics
Discover cloud computing forensics, exploring techniques, challenges, and tools used to investigate incidents and secure data in cloud environments.

Navigating Complexities with Private Case Management Services in India
Explore how private case management services in India streamline complex investigations, ensure discretion, and deliver strategic, result-driven solutions.
Unveiling the Enigmatic World of Audio Forensic Analysis Services
Audio forensic analysis is one field of investigative techniques that is frequently kept out of the public’s view. This complex

Unveiling the Intricacies of Chip-Off Mobile Forensics: Peering into Digital Worlds
Discover Chip-Off Mobile Forensics to extract data from damaged devices. Learn techniques, challenges, and its role in digital investigations.

ECS Delivers Innovative CSOC Coverage Solutions for Top Organizations in India
Discover how CSOC Solutions from ECS provide advanced threat monitoring, rapid response, and 24/7 security coverage for top organizations in

Discovering the Important Function of Disk Forensics Software Program in Cybersecurity and Data Recovery Solutions
Introduction In today’s ever-evolving landscape of cybersecurity threats, the importance of robust digital investigation methods cannot be overstated. One of
Unlocking the Secrets of Cell Phone Digital Forensics: Addressing Challenges, Threats, and Solutions
Cell phone digital forensics, also popularly referred to as mobile forensics, is the process of obtaining, extracting and analyzing digital

Navigating the Evolving Cyber Threat Landscape in 2026: Insights and Predictions
Explore the evolving Cyber Threat landscape in 2026 with key insights, trends, and predictions to help businesses stay secure and
Unveiling the Depths of Network Forensics: Exploring Investigation Techniques and Digital Solutions in India
In the detailed web of cyberspace, where details moves continuously exists the world of network forensics– an essential facet of

Unlocking the Critical Importance of Digital Cyber Forensics in India
Explore Digital Cyber Forensics in India. Learn its importance in solving cyber crimes, securing data, and supporting legal investigations nationwide.

Email Forensics: Complete Guide to Investigation, Analysis, Tools & Techniques
Learn email forensics, including forensic email collection, preservation, investigation techniques, analysis, tools and digital evidence handling.

Unveiling the Intricacies of Chip-Off Forensics in Mobile Device Investigations
Discover how Chip-Off Forensics helps recover data from damaged devices, revealing crucial evidence in mobile investigations and digital forensics.

Exploding the Code of Network Forensics: An Extensive Investigation
Introduction In the complex world of cybersecurity, network forensics sticks out as a keystone technique, encouraging private investigators to decipher

VAPT Cybersecurity Case Study: Infrastructure Security Testing for a Global IT Firm
Explore a VAPT cybersecurity case study for a global IT firm, covering infrastructure VAPT, network security testing, vulnerability assessment, penetration

Leveraging Social Media Forensic Services: A Guide to Uncovering Crucial Evidence
In today’s digital age, social media platforms have ended up being an important part of our lives forming exactly how

Unlocking Digital Clues: The Importance of Mobile Forensics and Professional Data Recovery Services in Investigations
Overview In today’s connected world where smart phones have actually ended up being expansions of our identifications, mobile forensics services

Unraveling Digital Crimes: The Power of Data Forensics Recovery
In today’s digitally linked globe, the increase in cybercrimes provides considerable difficulty to police and also cyber security specialists. Among

Enhancing Cybersecurity: The Role of Private Case Management Services and Digital Forensic Case Management
Introduction In the ever-evolving landscape of cyber security companies deal with a consistent hazard from cyber enemies looking for to

Safeguarding the Middle East: Navigating the Virtual Battlefield of Rising Cyber Threats
Explore rising Cyber Threats in the Middle East and strategies to strengthen cybersecurity, protect critical assets, and combat evolving digital

Securing Financial Solutions: A Deep Dive right into Cyber Safety Solutions together with Financial Fraud Investigation
Introduction In today’s digital driven age monetary solutions have actually gone through an innovative change inviting innovation to provide even

Navigating the Digital Landscape: The Importance of Data Recovery and Digital Forensics in Business
In the busy ever-evolving electronic landscape information is the lifeblood of companies and also people alike. From delicate client data

Unraveling the Digital Enigma: A Thorough Expedition of Disk Forensics in Cybersecurity
Explore disk forensics in cybersecurity, uncovering hidden data, investigative techniques, and tools used to solve digital crimes and protect systems

Eliminating VPS Hosting: A Comprehensive Guide to Making the Best Solutions
Explore VPS Hosting alternatives and smart solutions to improve performance, security, and scalability while choosing the best hosting strategy.

Unlocking Security: The Importance of Password Recovery Services and Expert Assistance
Introduction: In today’s digital age where individual as well as expert lives are elaborately woven right into the internet, the

Navigating the Digital Criminal Activity Scene: Recognizing Cloud Forensics in the Period of Cloud Computer
In the last few years business landscape has actually undertaken a considerable change with the extensive fostering of cloud-based solutions.

Navigating the Depths of Audio/Video Forensics with ECS Infotech’s Technological Edge
Introduction In the contemporary age of electronic interaction as well as multimedia investigatory examinations have actually advanced to satisfy the

Cyber Safety And Security Solutions: The Function of Cyber Investigatory Professionals in Protecting Digital Possessions
In the quickly advancing electronic landscape where technical innovations have actually reinvented the means we live as well as function

Unveiling the Secrets of Data Recovery: Navigating the Digital Maze with Forensic Precision
In our digital age, where information is the currency of power and communication, the need to safeguard, retrieve, and analyze

Navigating the Digital Battlefield: Unveiling the Power of Network Forensics in 2024
Introduction In the relentless evolution of the digital era, where the intertwining realms of business and technology have become inseparable,

Strengthening Cyber Fortifications: A Recap of the Cyber Security Awareness Event with Ahmedabad City and District Co-operative Bank Association
Explore the Cyber Security Awareness Event recap with insights on strengthening defenses, risk management, and security best practices for banks.

Unlocking Digital Realms: Navigating Password Recovery with Expertise and Tools
Discover expert techniques and advanced tools for Password Recovery, ensuring secure access and protection in today’s complex digital landscape.

Protecting Financial Fraud: Discovering Strategies and Solutions for Comprehensive Financial Fraud Recovery
Introduction: In the energetic scene of today’s computerized time, the approaching specter of monetary extortion postures an impressive danger to

Exploring the Digital Landscape: Mobile Forensics Services and Digital Solutions in the Modern Era
Introduction I the advanced commerce world, portable gadgets have ended up an vital portion of our everyday lives, serving as

Elevating Email Security: A Next-Gen Solution for Global Financial Services
Boost Email Security with next-gen solutions for global financial services, preventing phishing, fraud, and cyber threats with advanced protection.

Navigating the Future: Top 5 Data Center Trends Shaping 2026
Explore Data Center Trends for 2026, including AI, edge computing, sustainability, and automation transforming modern data infrastructure worldwide.

Leading Co-operative bank Opt ECS for CSOC Security Operation Center
Overview In today’s fast-paced digital landscape, businesses and organizations rely heavily on their IT infrastructure to stay competitive and secure.

Fortify Your Business Against Cyber Threats: The Power of Anti-Rogue and Anti-Phishing Services
In today’s digital landscape, the threats of rogue elements and phishing attacks have become increasingly sophisticated and prevalent. At ECS,

Navigating the Digital Frontiers: GCCI Features Mr. Vijay Mandora on Cyber Security Best Practices and Tips
Explore Cyber Security best practices and expert tips by Vijay Mandora in GCCI feature, covering strategies to safeguard digital assets

ECS Infotech Empanelled by SEBI to Provide Digital Forensics Services
Introduction Digital forensics is a critical component of modern financial regulation. In a world where financial transactions are increasingly conducted
Exploring Various Data Loss Scenarios and Safeguarding Your Business Against Them with ECS
Introduction In today’s digital age, data is the lifeblood of any business. Whether you are a small startup or a

10 Best Network Security Tools and Techniques to knows
Explore 10 essential Network Security Tools and techniques to protect systems, detect threats, and strengthen your organization’s cybersecurity defenses.

Maximizing IT Infrastructure Efficiency: A Case Study on Hyderabad Company Colocation with ECS
Discover how colocation improved IT infrastructure efficiency for a Hyderabad company with ECS, enhancing performance, scalability, and cost savings.

Enhancing Web Penetration for a Pune-Based Multilingual Communication Platform Provider
Boost Web Penetration for your Pune-based multilingual communication platform with proven strategies to expand reach, engagement, and growth online.
Safeguarding the Digital Realm: “How Advanced Forensics Shape Anti-Cybercrime Efforts in India”
Overview In an era dominated by technology, criminal behavior has shifted from conventional attacks to Cyber crimes, which can inflict

Top 7 Reasons Why MNC’s and SME’s Need VAPT
Discover why VAPT is essential for MNCs and SMEs. Learn 7 key reasons to strengthen security, identify vulnerabilities, and protect

ECS Cloud Security: Top 8 best practices for Secure VPS hosting
Learn secure VPS hosting with 8 ECS cloud security best practices to protect data, prevent threats, and ensure reliable, scalable

How Does Colocation Help To Reduce The Cost Of IT Infrastructure?
Discover how colocation reduces IT infrastructure costs with shared resources, lower maintenance, and scalable solutions for growing businesses.

Why Is Cybersecurity Important For Your Operational Technology Environment And How To Improve It?
Learn why Cybersecurity is crucial for OT environments. Discover risks, best practices, and strategies to improve Cybersecurity and protect operations.

Safeguard Your Mobile App’s Security With Mobile App Penetration Testing
Protect your app with Mobile App Penetration Testing. Identify risks, fix vulnerabilities, and strengthen mobile security for a safer user

Is ChatGPT a Boon or Curse? Cybersecurity Risks, Benefits & Limitations
Is ChatGPT safe to use? Explore ChatGPT's cybersecurity risks, limitations, benefits, privacy concerns and ways to use AI more securely.

What is the importance of Cyber Forensics?
Cyber Forensics helps investigate digital crimes, recover data, and ensure security. Learn why Cyber Forensics is vital for modern cybersecurity

Top 3 Reasons Why a Business Needs Advanced Network Firewall Security
Discover why Network Firewall Security is essential. Learn the top 3 reasons businesses need advanced protection to prevent threats and

Why Does an Organization Need a 24*7 Managed SOC Solution?
Discover why a Managed SOC Solution is vital for 24/7 threat monitoring, rapid incident response, and stronger cybersecurity protection for

The Ultimate Guide To Digital Forensics When It Is Needed?
Digital Forensics helps investigate cyber incidents, recover data, and preserve evidence. Learn when it’s needed and how it strengthens security

Why does your Organization need Email Security
Email Security is essential to protect your organization from phishing, malware, and data breaches. Learn why it’s crucial for modern

The Definitive Guide to Cyber Security Operation Center in 2026
Explore a complete guide to Cyber Security Operations Centers (CSOC), their roles, tools, and importance in protecting organizations from cyber

What Is Incident Response & Analysis? Why It Is Important For Any Law & Enforcement Agencies?
Learn what incident response & analysis is and why it is crucial for law enforcement agencies to handle threats, investigate

The Importance Of Cyber Security Within Your Organization
Protect your organization with strong cyber security. Learn why safeguarding data, systems & networks is vital to prevent threats and

SOC Framework – What Is It And How Does It Benefit Your Organisation?
Learn what a SOC framework is and how it benefits your organisation by improving threat detection, incident response, and overall

How does Digital Forensics Differ from Common Data Recovery?
Learn how digital forensics differs from data recovery in purpose, process, and legal use, from evidence analysis to retrieving lost

Pharmaceutical Companies Are At Higher Risk For Cybersecurity
Discover why pharmaceutical companies are prime targets for cyberattacks and how to strengthen data security, protect IP, and ensure compliance.

Why Is a Security Operations Center (SOC) Important for Business?
Learn why a Security Operations Center (SOC) is important for businesses, including SOC benefits, threat detection, monitoring, SOCaaS, services and

How to Protect Business From Data Threats? Secure your Office 365 emails and Google (G Suite) emails
Learn how to secure your Office 365 and Google Workspace emails from data threats with advanced protection, encryption, and best

Are You Cyber Secured
Wondering if you're cyber secured? Learn key cybersecurity tips, identify risks, and protect your data, devices, and online presence effectively

Why Cyber Security Services Required
Protect your data and systems with reliable cyber security services. Safeguard against threats and ensure business continuity with expert security

A Comprehensive VAPT Audit Service for Bangalore- Based IT company
Get a comprehensive VAPT Audit Service for Bangalore IT companies. Identify vulnerabilities, strengthen security, and ensure compliance today.

What are the different types of penetration testing?
Learn different types of penetration testing to identify vulnerabilities, improve security, and protect systems from cyber threats and attacks effectively.

Web VAPT for a leading SaaS provider Company
Overview The client offers a one-stop solution for each of the facilities necessary for startup companies and small and medium-sized

Top 3 cybersecurity threats for enterprise organizations
Discover top cybersecurity threats affecting enterprises and learn how to protect systems, data, and operations from evolving cyber risks and

ECS Secured Data Center: What is Data Center Security?
A Secured Data Center ensures data safety with advanced security, monitoring, and access control. Learn why a Secured Data Center

Managed VPS Hosting for Marketing Agencies: Features, Benefits & Real-World Case Study
Explore managed VPS hosting for marketing agencies and businesses in India. Learn about VPS performance, security, scalability, management and real-world

How to Protect Your Company from Future Cyber Breaches?
Learn how to prevent Cyber Breaches with strong security, monitoring, and risk management strategies to protect your company’s data and

What is Secured Cloud? How ECS Keep your organization’s Information Safe?
Secured Cloud solutions by ECS protect your organization’s data with advanced security, compliance, and reliable cloud infrastructure for safe operations.

Top Ransomware Attacks in India to Watch Out for in 2026
Stay alert to major Ransomware Attacks in India in 2026. Learn about emerging threats, cybersecurity risks, and ways to protect

Anti-Phishing Solutions for Banks & Cooperative Banks
Explore anti-phishing solutions for banks and cooperative banks, including phishing protection, rogue website detection, fraud monitoring and cybersecurity controls.

Top 5 Ransomware Attacks in India to Watch Out for in 2023
Explore major Ransomware Attacks in India, their impact on businesses, and how to stay protected against evolving cyber threats in

Web Application & Network VAPT of World Class Insurance Company
Web Application & Network VAPT helps insurance firms find vulnerabilities, secure systems, and prevent cyber threats to protect sensitive customer

VAPT Audit Services For A Multidisciplinary Construction Company
VAPT Audit Services help construction firms detect vulnerabilities, strengthen security, and protect critical data from cyber threats and breaches.

National Cyber Security Awareness Month – What are the impact of Cyber attacks on different Sectors?
National Cyber Security Awareness Month highlights how cyber attacks impact sectors like healthcare, finance, and manufacturing, stressing stronger security measures.

How VAPT Benefits the Healthcare Industry?
VAPT Benefits healthcare by identifying vulnerabilities, protecting patient data, and ensuring compliance with security standards to prevent cyber threats.
Cyber Forensics Solution Provided to a Manufacturing Company
Overview In today’s ever-changing and emerging technological world, Cyber forensics has become an important step in criminal investigations. This typically

How to choose Data Center Solution provider for your company?
Find the best Data Center Solution provider by evaluating security, scalability, and uptime to ensure reliable and efficient business operations.

What Is VAPT? Benefits, Services, Solutions & Why Organizations Need It
Learn what VAPT stands for, its benefits, services and solutions, and why organizations need vulnerability assessment and penetration testing to

Cyber Security Consulting Service to a Reputed Manufacturing Company
Overview Our client is in the manufacturing industry, and his company is in the emerging stage where they are growing

How Does VAPT Defend Against Data Breaches
VAPT helps identify vulnerabilities and prevent attacks. Learn how VAPT protects systems, reduces risks, and strengthens security against data breaches.

How ECS VPS Hosting Services Enhances Performance of ERP Solution Provider?
VPS Hosting Services enhance ERP solution performance with scalability, speed, and security, ensuring seamless operations and improved business efficiency.

All You Need To Know About VPS Hosting & Its Top 6 Features
Explore VPS Hosting and its top features. Learn how VPS Hosting improves performance, scalability, and control for websites and growing

ECS Provided a Complete CSOC Solution to a Bank
Overview Our client is a reputed industrialist and runs a co-operative bank. He has been working in the bank for

Top 6 Major Benefits Of Choosing Colocation Hosting Service
Discover the benefits of Colocation Hosting Service. Improve uptime, scalability, and security while reducing costs with reliable data center solutions.

How ECS Performed VAPT Testing for a Well-known Gaming Website?
Learn how VAPT Testing was performed for a gaming website by ECS. Discover methods used to identify vulnerabilities and strengthen

All You Need To Know About Data Center Tiers & Its Classification
Data Center Tiers explained—learn classification, uptime levels, and how each tier impacts reliability, performance, and infrastructure planning.

Why Web Application Vulnerability Assessment Penetration Testing is Important in 2022
Learn why web application VAPT is essential in 2022 to detect vulnerabilities, prevent cyberattacks, and ensure robust security for your

ECS Provided Data Center Solution to the Renowned Hardware Distributor
Discover how ECS delivered a scalable, secure data center solution to a renowned hardware distributor, boosting performance, efficiency, and growth.

How to Choose the Best VPS Hosting Plan for Your Business
Compare VPS hosting plans, features, pricing, managed vs unmanaged VPS and resources to choose the best VPS hosting plan for

How ECS Helped Retrieve Deleted WhatsApp Chat Messages For a Law Enforcement Agency?
TABLE OF CONTENTS Case Overview Case Challenges How did ECS Provide a Solution? Result Conclusion Case Overview Client is a

National Cybersecurity Awareness Month: What every organization should know about Cyber Risk & IoT Security?
Learn what every organization must know about cyber risk and IoT security this Cybersecurity Awareness Month to protect data, devices,

Mobile App VAPT: Complete Android Application Security Testing Guide
Learn how mobile app VAPT works, including Android security testing, vulnerability assessment, penetration testing, key risks, tools, process and best

How ECS Channel Partner Program proved to be beneficial to a business service provider in Gujarat ?
Explore how the ECS Channel Partner Program helps business service providers in Gujarat grow revenue, expand services, and gain a

ECS data center have best-in class physical security standards – All about Data center physical security
Discover how ECS data centers ensure best-in-class physical security with advanced surveillance, access control, and strict safety protocols.

ECS’ audio and video forensics expertise helped a law enforcement agency with face recognition of the culprit.
Case Overview: The customer require audio-video evidence from the scene of the crime. Our client is one such law enforcement

How to improve your IT and network security with VAPT?
Learn how VAPT strengthens IT and network security by identifying vulnerabilities, reducing risks, and protecting systems from cyber threats effectively.

How Kaspersky Endpoint Security Solution Was Used To Strengthen Network Security
Company Overview: The client is a leading technology solutions provider offering services in mobile and web applications and enables businesses

Cybersecurity threats for SMEs
Explore key cybersecurity threats for SMEs, including phishing, ransomware, and data breaches, and learn how to protect your business effectively.

Clinical Research Organisation Chooses ECS’ Email Security Solution to Protect Confidential Data and Combat Malicious Intrusions via Emails.
Company Overview: Client is an independent clinical research organisation that creates in-depth scientific know-how, technical edge and better foresight for

5 Tips And Best Practices For Mitigating Cloud-Related Cybersecurity Risks
Learn 5 proven tips and best practices to mitigate cloud cybersecurity risks, strengthen data protection, and ensure secure cloud operations

IT infrastructure and audit services for a global enterprise that spans 4 continents
Ensure seamless IT infrastructure and audit services for global enterprises across 4 continents with enhanced security, compliance, and performance.

Top 8 Organizational Benefits of Using a VPS Hosting
Explore the top 8 benefits of VPS hosting for organizations, including scalability, security, performance, and cost-efficiency for growing businesses.

Continuous VAPT for SMEs: Why Ongoing Security Testing Matters
Learn why continuous VAPT is important for SMEs, including vulnerability scanning, penetration testing, cloud security, CI/CD and ongoing risk management.

Major Financial Services Company Choses ECS Deception For Visibility And Forensics
Overview The CISO required better visibility into their large and diverse international network that spanned corporate and remote offices. Like

ECS Cloud VPS Hosting Service levelled up the flexibility & performance of the server of the Well-known Healthcare Organization
Discover how ECS Cloud VPS hosting improved flexibility, scalability, and performance for a leading healthcare organization’s critical server systems.

Significance of Tier 4 Data Center
Understand the importance of Tier 4 data centers, offering maximum uptime, fault tolerance, and high security for critical business operations.

Large Co-operative Bank Was Secured By ECS Mobile Device Management
Overview This Bank has a spectacular growth in the nearly 40 years of time span having more than 20+

7 Common Mobile Threats That Can Risk Your Organization In 2021
Discover 7 common mobile threats that put organizations at risk in 2021, including malware, phishing, and unsecured apps impacting business

Cyber Security’s Resolutions heading our way in 2021
Explore key cybersecurity resolutions shaping 2021, from stronger data protection to zero trust adoption and enhanced threat detection strategies.

Secure Work From Home Solutions helped Software Development Organization to mitigate from data breach
Discover how secure work-from-home solutions helped software development firms prevent data breaches and protect sensitive data during remote operations.

Cybersecurity in BFSI: Cyber Threats, Risks, Solutions & Prevention
Explore cybersecurity in BFSI, including banking cyber threats, real-time detection, prevention, MDR, dark web monitoring, compliance and security solutions.

Ransomware Attack On Notable Pharmaceutical Company
Explore a ransomware attack on a notable pharmaceutical company, its impact on operations, data security risks, and key lessons for

National Cybersecurity Awareness Month- October 2020: 8 Important Cyber Security tips
Celebrate National Cybersecurity Awareness Month 2020 with 8 essential tips to protect your data, prevent cyber threats, and enhance online

Cyber Security Risk Management During COVID-19 Pandemic
Learn how to manage cyber security risks during COVID-19 with remote work protection, data security strategies, and threat mitigation best

Why to choose ECS Tier-4 Data Centre?
Discover why ECS Tier-4 Data Centre is ideal for your business with maximum uptime, robust security, redundancy, and reliable infrastructure

ECS ensured Hassle-Free Colocation/ Data Center Solution for re-known Automobile Distributor
ECS ensures seamless colocation and data center solutions for a leading automobile distributor with high uptime, security, and scalability.

Are You Cyber Secured?
All the small businesses, as well as large enterprises, face cybersecurity challenges, which means they are proactively protecting organizational assets,

Chinese Cyber-attacks: Indian Firms on Alert, Vulnerabilities Amid by China’s Cyber Threat
Rising Chinese cyber threats put Indian firms on alert. Explore vulnerabilities, risks, and measures businesses can take to strengthen cybersecurity

International Yoga Day 2020: A day to hang out with your soul
Celebrate International Yoga Day 2020 by reconnecting with your inner self. Discover mindfulness, peace, and wellness through yoga practice.

Cyber-Solutions during Global Pandemic
Explore how cyber solutions enabled businesses to adapt, secure data, and maintain operations during the global pandemic and beyond.

Cyber-security Audit helped Ahmedabad Based Manufacturing Company from future Cyber Threat | VAPT
See how a cyber security audit and VAPT helped an Ahmedabad manufacturing company prevent future threats, strengthen defenses, and secure

Why Deception as a Cyber Security Defense?
Learn why deception is a powerful cyber security defense. Detect threats early, mislead attackers, and strengthen protection against advanced cyber

SAP Application & Hosting
Client: Arunachal Logistics Pvt. Ltd SERVICES USED: SAP APPLICATION HOSTING IDC & MANAGED HOSTING SERVICES SAP hosting services from ECS enable

Disaster Recovery Services for Chemical Manufacturing Company at Baroda: Gulbrandsen Technologies for SAP
Reliable disaster recovery for SAP at Gulbrandsen Technologies, Baroda. Ensure business continuity, data protection, and minimal downtime in manufacturing.

Does your business require Cyber Security Services protecting against Spyware, Viruses and other online threats?
Protect your business from spyware, viruses, and online threats with advanced cyber security services. Ensure data safety and uninterrupted operations

Make Your Bank Cyber Secure
Strengthen your bank’s cyber security with advanced protection against threats, fraud, and data breaches. Safeguard transactions and customer trust.